· Digital Footprint Check · Content Marketing · 13 min read
Browser Privacy Settings How to Lock Down Every Browser
Master browser privacy settings with step-by-step guides for Chrome, Firefox & Edge. Learn what each control does and how to verify your privacy.
You open a browser to check one product, sign in to email, watch a video, and search for a health question. By the end of the session, the browser may hold login cookies, browsing history, site permissions, cached files, and account-linked activity. None of this feels dramatic while it happens, but it creates a detailed trail that can affect your online identity, account security, and reputation.
Browser privacy settings give you a practical control layer. They won't make you invisible, and they can't erase information a website already collected, but they can limit how much your browser stores, shares, and reveals during everyday browsing. The most useful approach combines careful configuration, regular verification, and monitoring of information already exposed elsewhere.
Why Your Browser Is Your Biggest Privacy Exposure
Your browser looks like a window, but it also acts as a local record keeper and permission manager. It remembers which sites you visit, stores data that keeps accounts signed in, accepts cookies from pages and embedded services, and asks whether websites can use your camera, microphone, location, or notifications.
Consider a normal evening. You search for a pair of running shoes, visit a retailer, read a review on another site, and sign in to a shopping account. First-party data may help the retailer remember your basket or language preference. Third-party services embedded across websites may also attempt to recognize the browser beyond the original site. The distinction matters because third-party cookies are designed to let one site track activity across other sites.
The footprint extends beyond browsing history
Clearing history removes a visible list from your device. It doesn't necessarily revoke a site's stored permissions, delete cookies from every service, remove account activity saved by Google, or take down information published in public records and breach databases.
That difference creates practical risks:
- Job prospects: A public username, old profile, or exposed comment can connect your professional identity to activity you forgot existed.
- Scam prevention: Attackers can combine exposed usernames, email addresses, and account clues to make phishing messages feel personal.
- Identity theft: Browser hygiene won't remove breached information, but it can reduce additional local storage and unnecessary account exposure.
- Gaming and dating safety: Shared devices, persistent sessions, and location permissions can reveal more than you intended to friends, strangers, or abusive contacts.
A browser privacy setting is an active choice. Leaving a default permission untouched is usually a passive choice, even when the browser presents it as convenient.
Practical rule: Treat every browser as a separate privacy environment. A setting changed on your laptop won't automatically protect a different browser profile or phone.
Major browsers provide controls to pause activity saving, clear browsing data, manage cookies, and review site permissions. Microsoft documents these controls through its browser data and privacy guidance, while Google's account privacy controls can pause the saving of Search and browsing activity. For a broader explanation of how ordinary browsing contributes to exposure, read how your browsing habits reveal more than you think.
What Every Browser Privacy Setting Actually Controls
The labels differ between Chrome, Firefox, Edge, Safari, and mobile browsers, but the underlying controls are familiar. Learn what each one changes before selecting the strictest option.
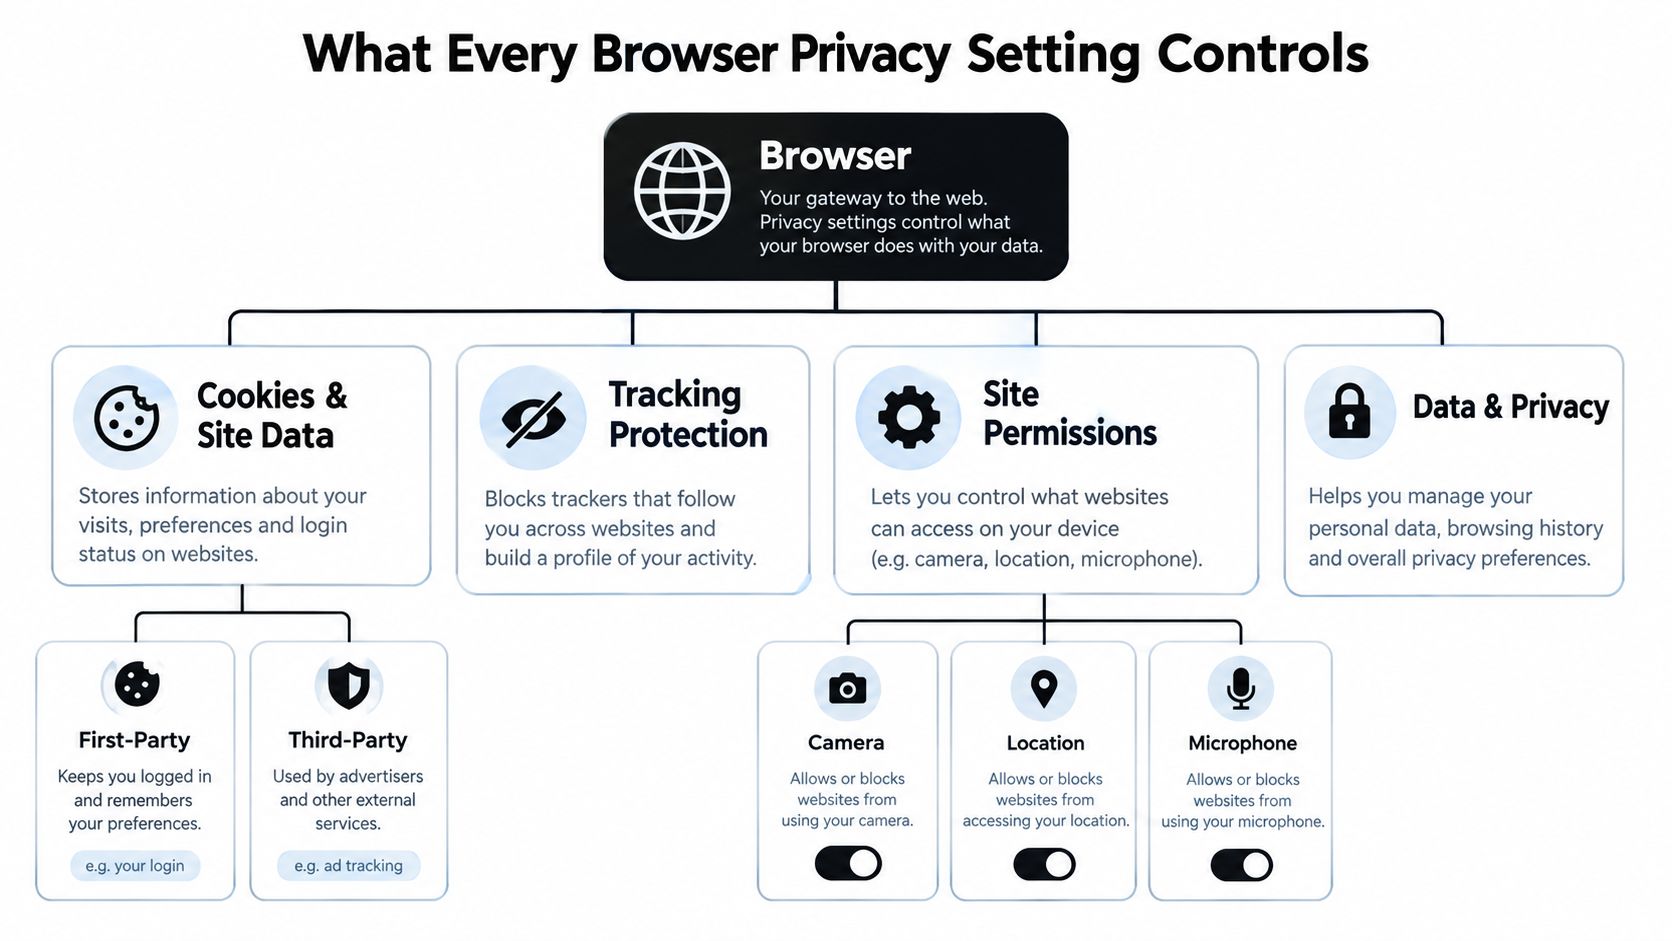
Cookies and site data
A first-party cookie comes from the site shown in your address bar. It can preserve a login state, shopping basket, language choice, or other preference. Blocking or deleting every first-party cookie improves local privacy but can sign you out and make familiar websites behave as though you're visiting for the first time.
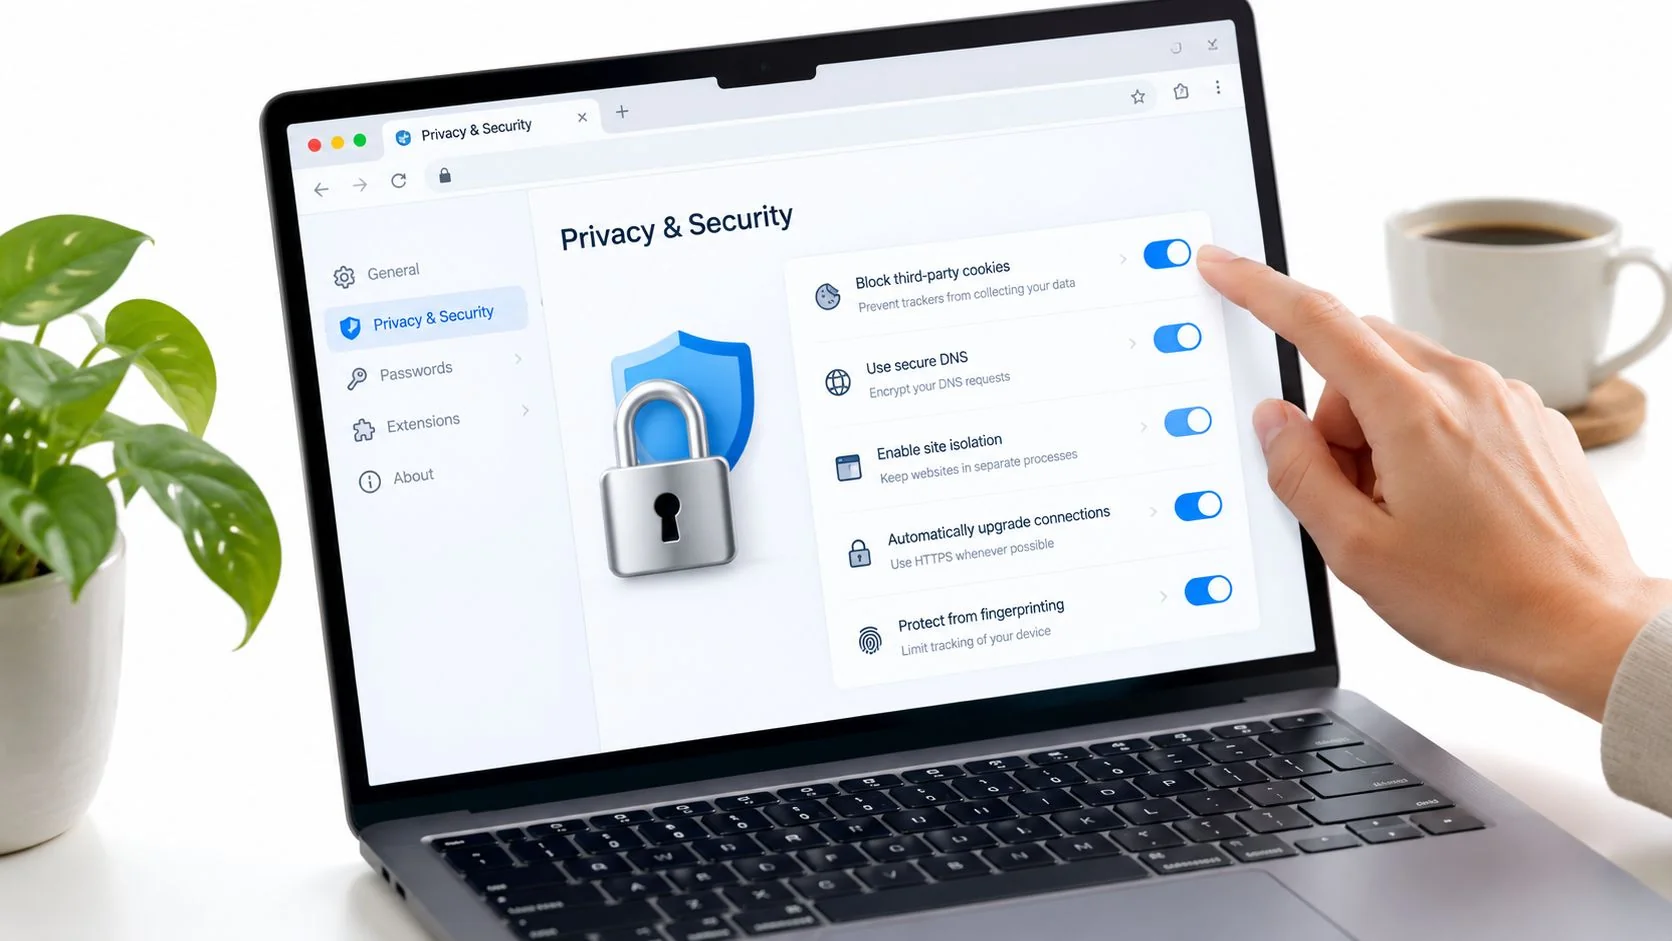
A third-party cookie comes from a different service embedded in the page, such as an advertising, analytics, video, or social media provider. Blocking it limits a common way for one service to recognize activity across unrelated websites. It doesn't stop the original site from recording activity on its own systems, and it doesn't eliminate other tracking techniques.
A large-scale measurement of one million sites found that Firefox's third-party cookie blocking left only 237 sites, or 0.4%, with any third-party cookies set from a non-landing-page domain. The same report found that Ghostery reduced average third-party includes from 17.7 to 3.3, with only 0.3 of those having third-party cookies and 0.1 having identifiers. These figures come from the browser privacy measurement report, and they illustrate why third-party cookie controls deserve priority.
Tracking protection
Tracking protection blocks or limits known trackers, often including scripts and resources that observe activity across sites. It works alongside cookie controls, not instead of them. A tracker may still identify a browser through URL parameters, account logins, local storage, or fingerprinting.
Fingerprinting uses signals such as browser configuration, device characteristics, fonts, and screen details to make a browser more recognizable. Privacy tools can reduce fingerprinting, but they don't remove it entirely. An academic evaluation found that Chrome and Edge exposed consistently richer fingerprints, while Tor and Brave provided stronger protections through spoofing. The academic evaluation of the illusion of privacy settings also warns that a setting may lower fingerprint consistency without making tracking disappear.
Permissions and stored activity
Site permissions decide whether a website can request sensitive device features. Camera and microphone access matter during video calls, but a forgotten permission can create unwanted exposure. Location access can reveal a precise place when a general region would be enough. Notifications can become a channel for spam, misleading alerts, or social engineering.
Data controls cover history, cached files, downloads, cookies, and other stored content. Account activity controls cover information saved beyond the browser, such as Search or browsing activity associated with a Google account. Deleting local data won't automatically remove account records, and pausing account activity won't clear cookies already stored on the device.
For a practical explanation of private browsing's limits, use this guide to private browsing. Private windows can reduce local history storage, but they aren't a substitute for blocking unwanted trackers, limiting permissions, or checking what websites retain.
You can also watch this visual walkthrough before changing settings:
How to Configure Privacy Settings in Chrome Firefox Edge and Mobile
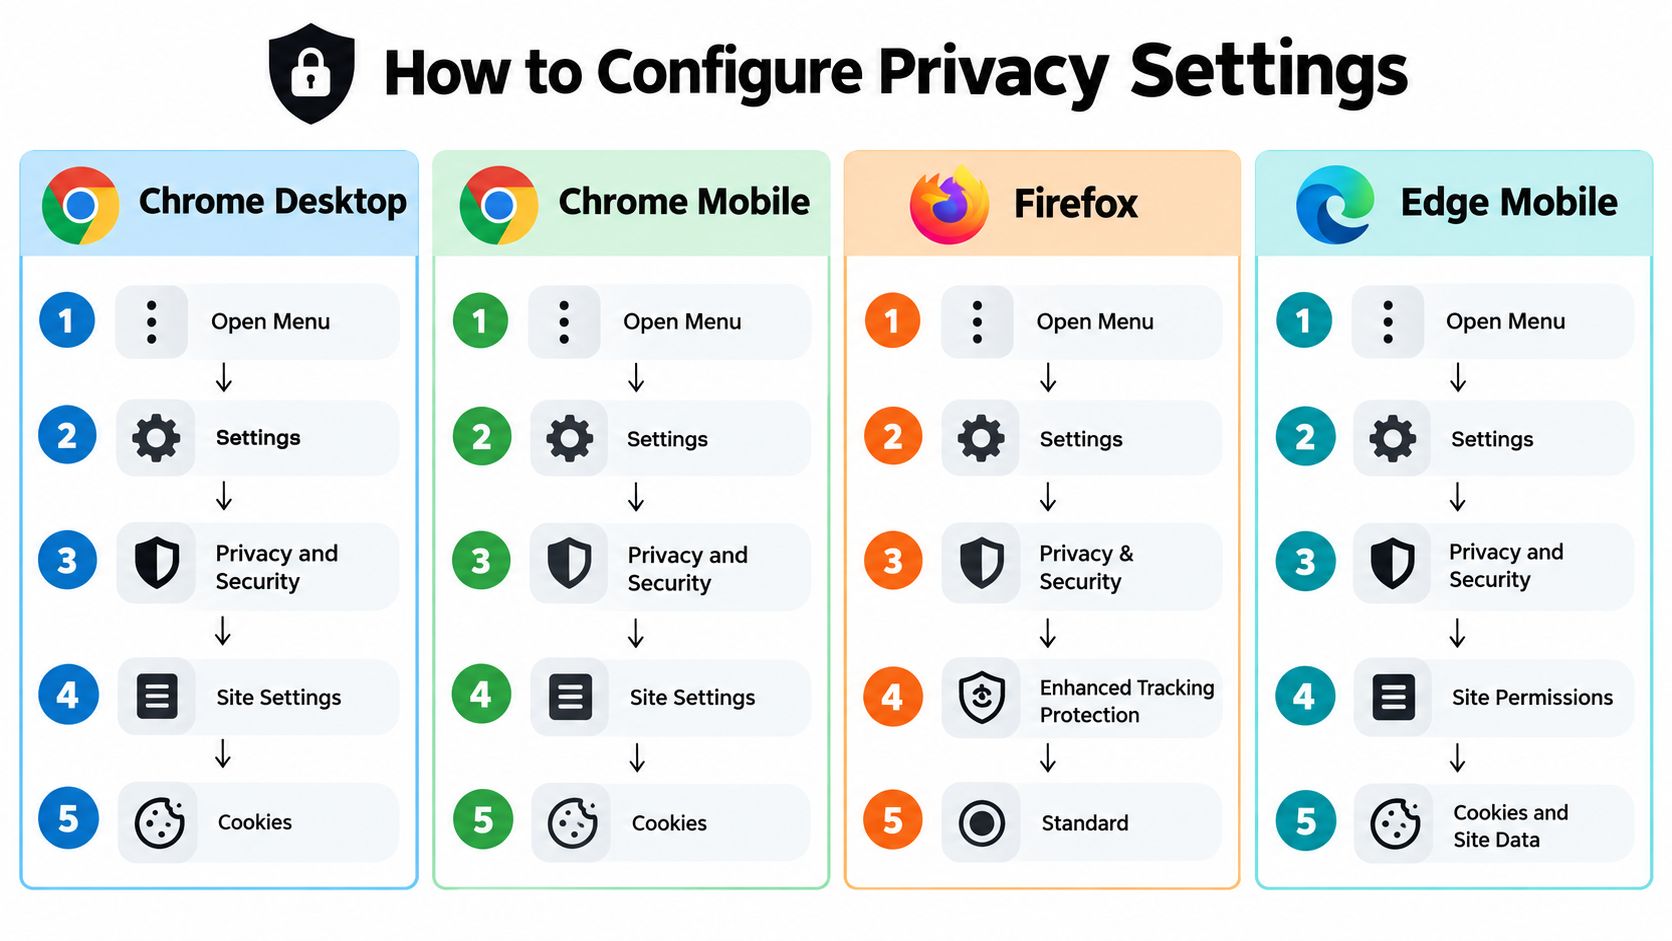
Menu names can change slightly between versions, but the privacy categories remain recognizable. Change one browser at a time, then test a site you use regularly.
Chrome on desktop
Open the three-dot menu, choose Settings, then Privacy and security. Open Third-party cookies and select the blocking option that prevents third-party cookies. Chrome also provides a separate Tracking Protection area on newer builds, so review it rather than assuming cookie blocking covers every tracker.
Under site data and permissions, inspect saved data by site. Delete everything only when you're prepared to sign in again, or remove individual domains when a single account is causing concern. For account-linked activity, open Google's privacy controls and pause Search or browsing activity if you don't want it saved to that account.
Chrome's site settings also provide a Reset permissions button. Use it after a period of heavy browsing, when you no longer remember which sites can access your camera, location, microphone, or notifications. Google's Chrome site settings documentation explains how to review stored data and change permissions per site.
On Android, open Chrome, select the three-dot menu, choose Settings, then Privacy and security or Site settings. Review cookies, permissions, and notifications individually. On iPhone and iPad, Chrome's controls work within Apple's permission system, so also review the device's app permissions in system settings.
Firefox
Open the menu, select Settings, and choose Privacy & Security. Firefox's Enhanced Tracking Protection offers Standard, Strict, and Custom modes. Standard is a sensible starting point. Strict blocks more trackers and third-party cookies, but Firefox warns that blocking all third-party cookies can break parts of some websites.
Custom mode is useful when you want precision. Mozilla describes four relevant cookie-blocking levels, from blocking cookies from third-party trackers through blocking all third-party cookies and, at the most restrictive end, all cookies. Choose the narrowest option that solves your concern, then add an exception only for a trusted site that needs it. Mozilla's Firefox tracker-control explanation details these tradeoffs.
Firefox also includes controls for clearing cookies and site data, managing permissions, and sending a Global Privacy Control signal requesting that websites not sell or share personal data or use it across contexts for targeted advertising. On mobile, open the Firefox menu, enter Settings, and look for Tracking Protection, Data Management, and site permissions.
Edge
In Edge, open the three-dot menu, choose Settings, and select Privacy, search, and services. Review Tracking prevention, then choose Balanced for a practical starting point or Strict when you're willing to troubleshoot more often. Edge also exposes cookie controls and a way to clear browsing data when the browser closes.
Under Cookies and site permissions, inspect camera, microphone, location, and notification access. Edge includes its own Reset permissions control, which can restore defaults after you remove access from sites you no longer trust.
Edge Mobile and Chrome Mobile share similar concepts, but don't assume a desktop change carries over. Check the mobile browser's settings, then inspect Android or iOS system permissions. If you manage browsers for work devices, you can find a browser for your company by comparing compatibility, administrative controls, and privacy features before standardizing on one.
Finally, clear tracking data deliberately rather than reflexively. This guide to deleting tracking cookies can help you choose between removing one site's data and clearing the entire browser store.
Choosing the Right Privacy Level Without Breaking Websites
Privacy isn't a contest to see who can enable the most restrictive switch. A setting is useful when it reduces exposure without making you abandon the protection because essential sites stop working.
Blocking third-party cookies usually targets cross-site recognition. Strict tracking protection goes further by blocking more trackers and resources. Blocking all cookies can affect logins, embedded payment tools, video players, shopping carts, and identity checks. The right choice depends on whether you're protecting a shared device, managing a sensitive account, or reducing routine advertising surveillance.
Browser Privacy Levels Compared
| Configuration | What It Blocks | Breakage Risk | Best For |
|---|---|---|---|
| Default | Basic browser protections and some known tracking defenses | Lower | Users who need maximum compatibility |
| Balanced | Third-party cookies and common trackers, depending on the browser | Moderate | Everyday browsing with useful privacy gains |
| Strict | More trackers, third-party cookies, and restrictive site behavior | Higher | Sensitive browsing and users willing to troubleshoot |
| Custom | Selected cookie categories, trackers, and permissions | Variable | People who want control by site or category |
Firefox Custom mode is particularly useful when a blanket setting causes trouble. You might block cookies from third-party trackers while allowing a trusted service to use necessary first-party cookies. Edge provides tracking exceptions, and Chrome lets you manage site data and permissions by domain.
The most private setting you can keep enabled is better than a strict setting you immediately disable.
Fingerprinting changes the decision. Even after cookies are blocked, a browser can still expose a recognizable combination of configuration signals. Research on fingerprinting shows why a layered approach works better than one toggle: choose a browser with stronger protections, enable tracking defenses, minimize permissions, and verify results across sessions.
An IP-hiding feature addresses network visibility, not every browser signal. If you're trying to reduce network-based exposure as well, review this explanation of how to hide your IP address, while remembering that it doesn't replace cookie, permission, or fingerprint controls.
If a site breaks, don't restore every default immediately. First allow only the specific permission or cookie behavior the site requires, use a separate browser profile for that service, and retest after a reload. This preserves stricter protection for the rest of your browsing.
How to Verify Your Browser Privacy Settings Are Working
Configuration is only the first half of the job. A browser update, synchronized profile, extension, or site exception can change the result, so verification should be part of your routine.
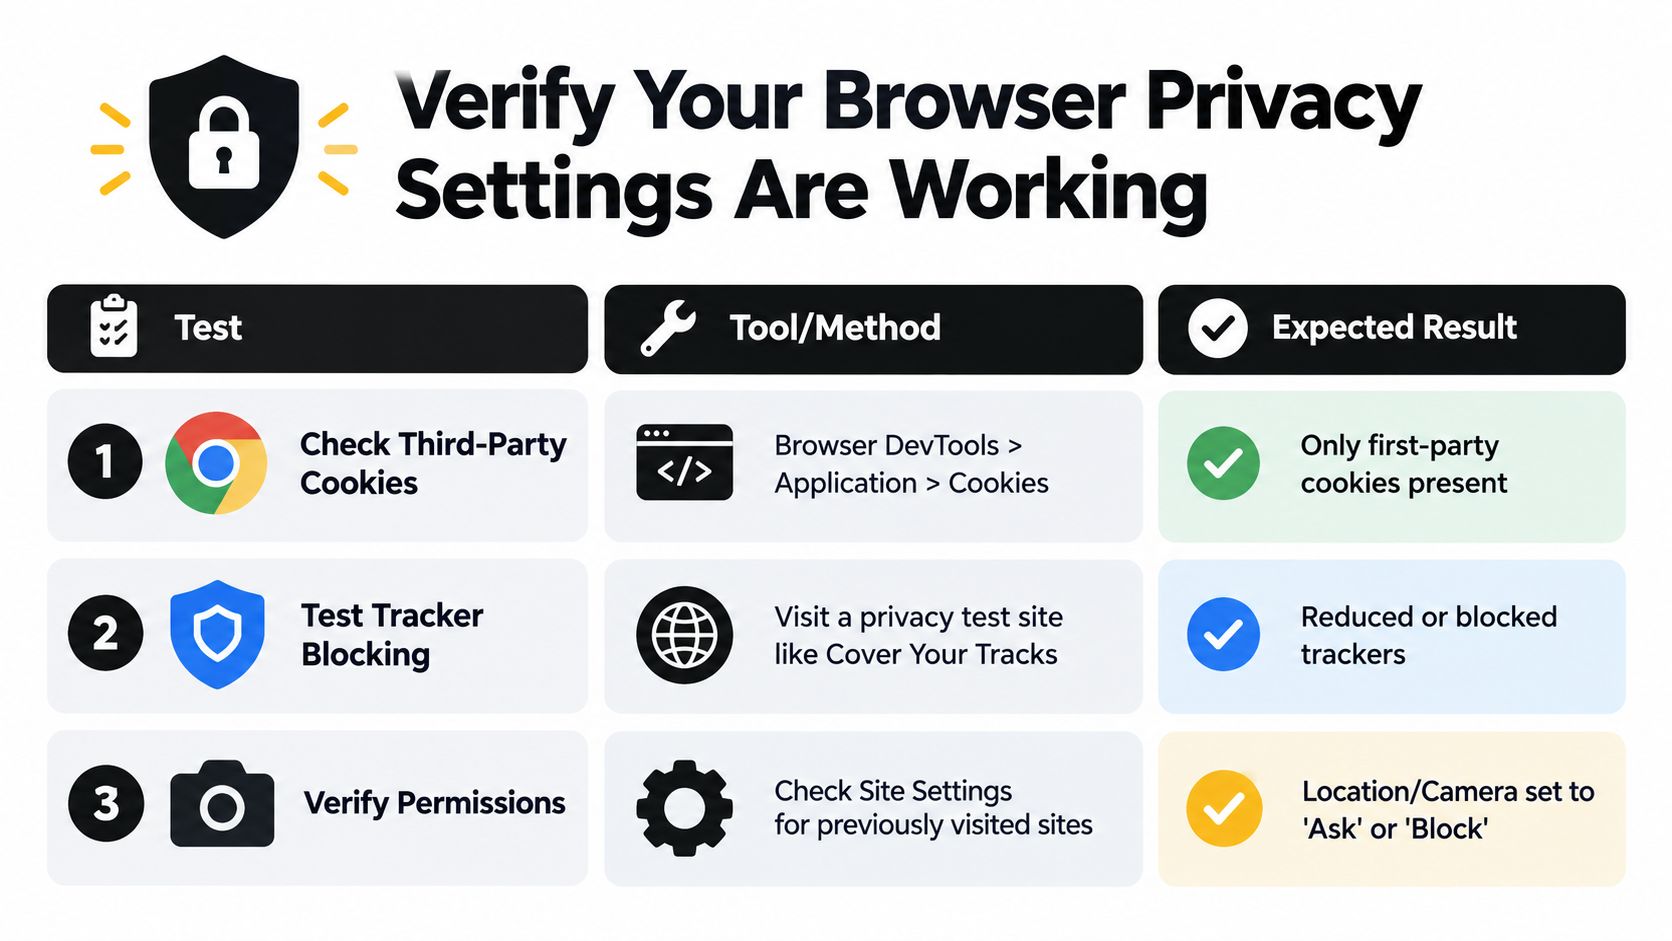
Start with site data. Open the browser's site settings for a website you just visited and review cookies, local storage, permissions, and notifications. After blocking third-party cookies, reload the page and inspect whether unrelated advertising or analytics domains still set cross-site cookies or identifiers. Repeat the check after signing in and opening a new page, because login flows often change what a site requests.
A large-scale browser privacy report recommends this practical sequence: disable third-party cookies, add tracker-blocking extensions, then verify whether common ad and analytics domains continue setting cross-site cookies or identifiers after login sessions and page reloads. Don't treat one successful test as proof that every site behaves the same way.
A simple verification routine
- Review permissions: Visit the browser's site settings and check previously visited sites. Set camera, microphone, location, and notifications to Ask or Block unless you have a clear reason to allow them.
- Test tracker behavior: Use a reputable privacy testing page and compare results after changing one control. Look for reduced tracker activity, not a claim of total anonymity.
- Check fingerprint stability: Use fingerprint-testing pages across separate sessions. If the same device and browser signals remain highly consistent, cookie blocking alone hasn't solved fingerprint exposure.
- Confirm clearing behavior: Close and reopen the browser, then check whether selected history, cookies, or site data were removed.
The UK government-backed BIT report found that participants spent an average of 17 seconds interacting with browser-level cookie settings. That short interaction highlights a real usability problem, not a personal failure. The BIT browser cookie settings report supports taking a deliberate pause before accepting a privacy choice.
Incognito isn't a verification method. Google documentation says Incognito blocks third-party cookies by default, and Google's Privacy Sandbox update discusses planned IP Protection rollout, but neither removes the need to inspect permissions, stored data, and fingerprint behavior. If settings appear to revert, check synchronized browser profiles, site-specific exceptions, extensions, and whether you're testing a different browser or device.
Your Ongoing Privacy Checklist and Next Steps
Browser privacy settings need occasional maintenance because your browsing pattern changes. A site that needed location access for a one-time task may retain that permission until you revoke it, and a forgotten login can remain active through stored cookies.
Use this compact review habit:
- Check permissions: Reset camera, microphone, location, and notification access for sites you no longer use.
- Review site data: Remove cookies and storage from sensitive or abandoned accounts, choosing individual sites when you want to avoid signing out everywhere.
- Revisit tracking controls: Confirm third-party cookies remain blocked and that your selected tracking mode still matches your tolerance for site breakage.
- Test after updates: Recheck cookie behavior and fingerprint signals after major browser changes or when a familiar site starts behaving differently.
- Audit the wider footprint: Look beyond the browser for exposed usernames, email-linked accounts, gaming profiles, professional pages, breach records, and public records.
Browser controls reduce what happens during browsing. They can't show you every profile, old account, or exposed record already connected to your name, email, phone number, or username. Digital Footprint Check searches 500+ platforms, including social networks, breach databases, gaming profiles, professional networks, and public records, so it can serve as a separate discovery and monitoring layer rather than a replacement for browser configuration.
For a printable routine, use this free privacy checklist. Pairing it with periodic footprint reviews helps you spot risks that browser controls can't reach, including old dating profiles, gaming accounts, public contact details, and information that could affect work or personal safety.
Small changes add up. Block cross-site cookies, reduce permissions, verify the result, and review what the wider internet already exposes about you.
Digital Footprint Check helps you discover exposed personal information across social platforms, breach databases, gaming profiles, professional networks, and public records. Visit Digital Footprint Check to run a free check and use what you find to guide your next browser privacy and account-security decisions.