· Digital Footprint Check · Content Marketing · 14 min read
Data Breach Response Plan: a Practical Guide
Write a data breach response plan with named roles, 72-hour notices, and monitoring. Speed can cut about $1.14 million.
A breach lasting more than 200 days cost approximately USD 1.14 million more, on average, than one lasting less than 200 days, according to IBM's 2025 Cost of a Data Breach Report. That difference reframes a data breach response plan: it's not paperwork you finish after an attack, but a way to remove delays while someone may still have access.
For a small team, the useful version names who can act, what they can approve, and how they'll know an action worked. It also follows the consequences beyond company systems, helping affected people protect reused work, social, gaming, dating, and financial accounts.
What Your Data Breach Response Plan Must Include
Start with a one-page map that a responder can use under pressure. Fill in the owner and completion condition before writing detailed procedures.
Four phases of a data breach response plan
| Phase | Owner | Main work | Done when |
|---|---|---|---|
| Preparation | Incident lead | Train the team, set decision rights, keep contacts and logs | Roles accepted and contacts tested |
| Detection and analysis | On-call security or IT | Triage alerts, confirm scope, preserve evidence | Incident declared and logs held |
| Containment, eradication, and recovery | Technical lead with IT and business owners | Isolate systems, disable stolen credentials, remove bad access, restore from a clean backup | Attacker path closed and services verified |
| Post-incident activity | Incident lead with legal | Record cause and cost, meet notice duties, fix controls | Lessons written back into the plan |
Separate readiness from crisis work
Preparation means giving people authority before they need it. The incident lead arranges training, working contact details, protected logs, and access to outside help.
Detection and analysis turns an alert into an evidence-backed decision. The investigator records what happened, identifies affected accounts and systems, and preserves evidence before anyone wipes a device.
Containment, eradication, and recovery combines stopping access, removing the cause, and restoring trustworthy operations. The technical lead closes the attacker's entry route and checks the restored service rather than assuming a successful backup restore means everything is safe.
Post-incident activity converts the experience into changes someone owns. The incident lead records causes and costs, tracks notification duties, and assigns corrective work.
These four grouped phases follow NIST Special Publication 800-61 Revision 2, published in August 2012 and withdrawn on April 3, 2025, after Revision 3 superseded it. Use this historical framework to organize responsibilities, not as a substitute for reviewing current guidance.
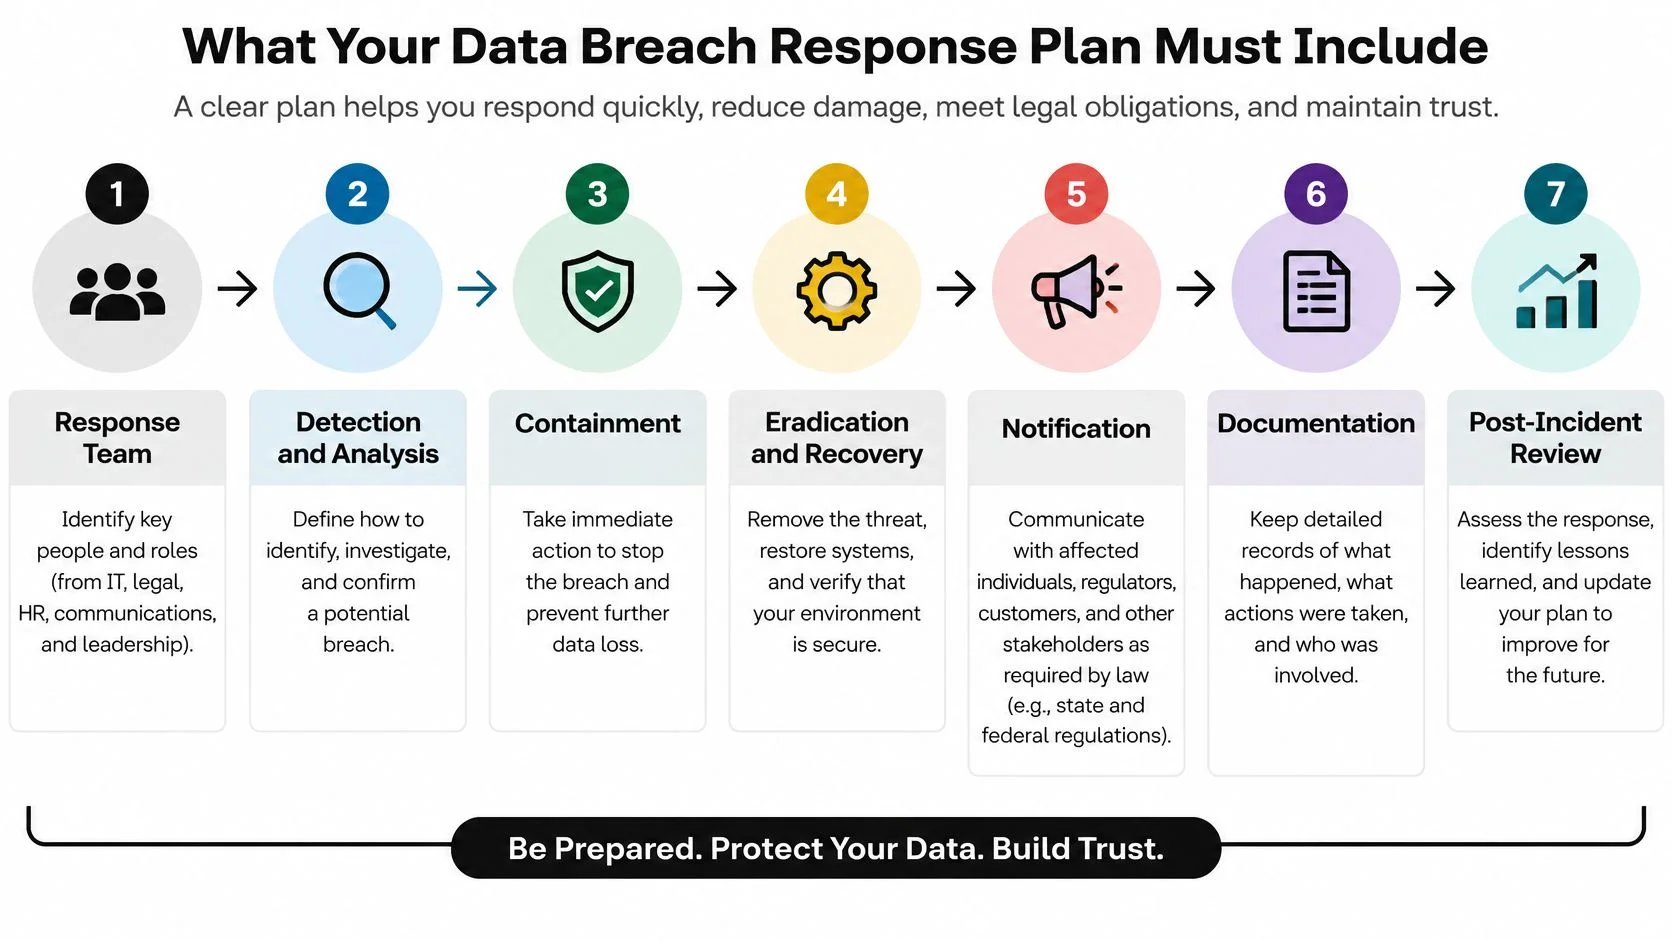
This visual provides another way to organize the practical tasks.
Define what the plan protects
Include hosted services, employee devices, vendor access, and identity systems, not just the customer database. An attacker who controls email may intercept recovery messages even after you repair another application.
Sector-specific material can help identify missing dependencies. For care providers, RDE Technologies' resource on HIPAA IT safeguards for nursing homes offers context for discussing healthcare IT protections with their provider; counsel should separately assess legal obligations.
Practical rule: A phase needs a named person and an observable completion condition. A department name and “resolved” aren't enough.
Breach Cost Differences by Response Speed
The cost gap between shorter and longer breaches gives managers a reason to fund readiness. It doesn't mean a particular response action guarantees a particular saving.
IBM's study covered 600 organizations breached between March 2024 and February 2025. The benchmarks describe that study population, not a forecast of what a small business will lose.
2025 breach cost and speed benchmarks
| Measure | Figure | What it means for the plan |
|---|---|---|
| Global average breach cost | USD 4.44 million | Down from USD 4.88 million in 2024 |
| Lifecycle under 200 days | USD 3.87 million | Shorter incidents cost less in the study |
| Lifecycle over 200 days | USD 5.01 million | About USD 1.14 million more than the short lifecycle |
| Average identify-and-contain time | 241 days | Down from a 287-day peak in 2021 |
| Internal team identification | 172 days | Six days faster than the prior year |
| Extensive AI and automation | 80 days faster and USD 1.9 million less | Supports investment in tested, pre-approved workflows |
These are IBM's reported benchmarks from the study linked above. Internal security teams also contained breaches two days faster than the prior year.
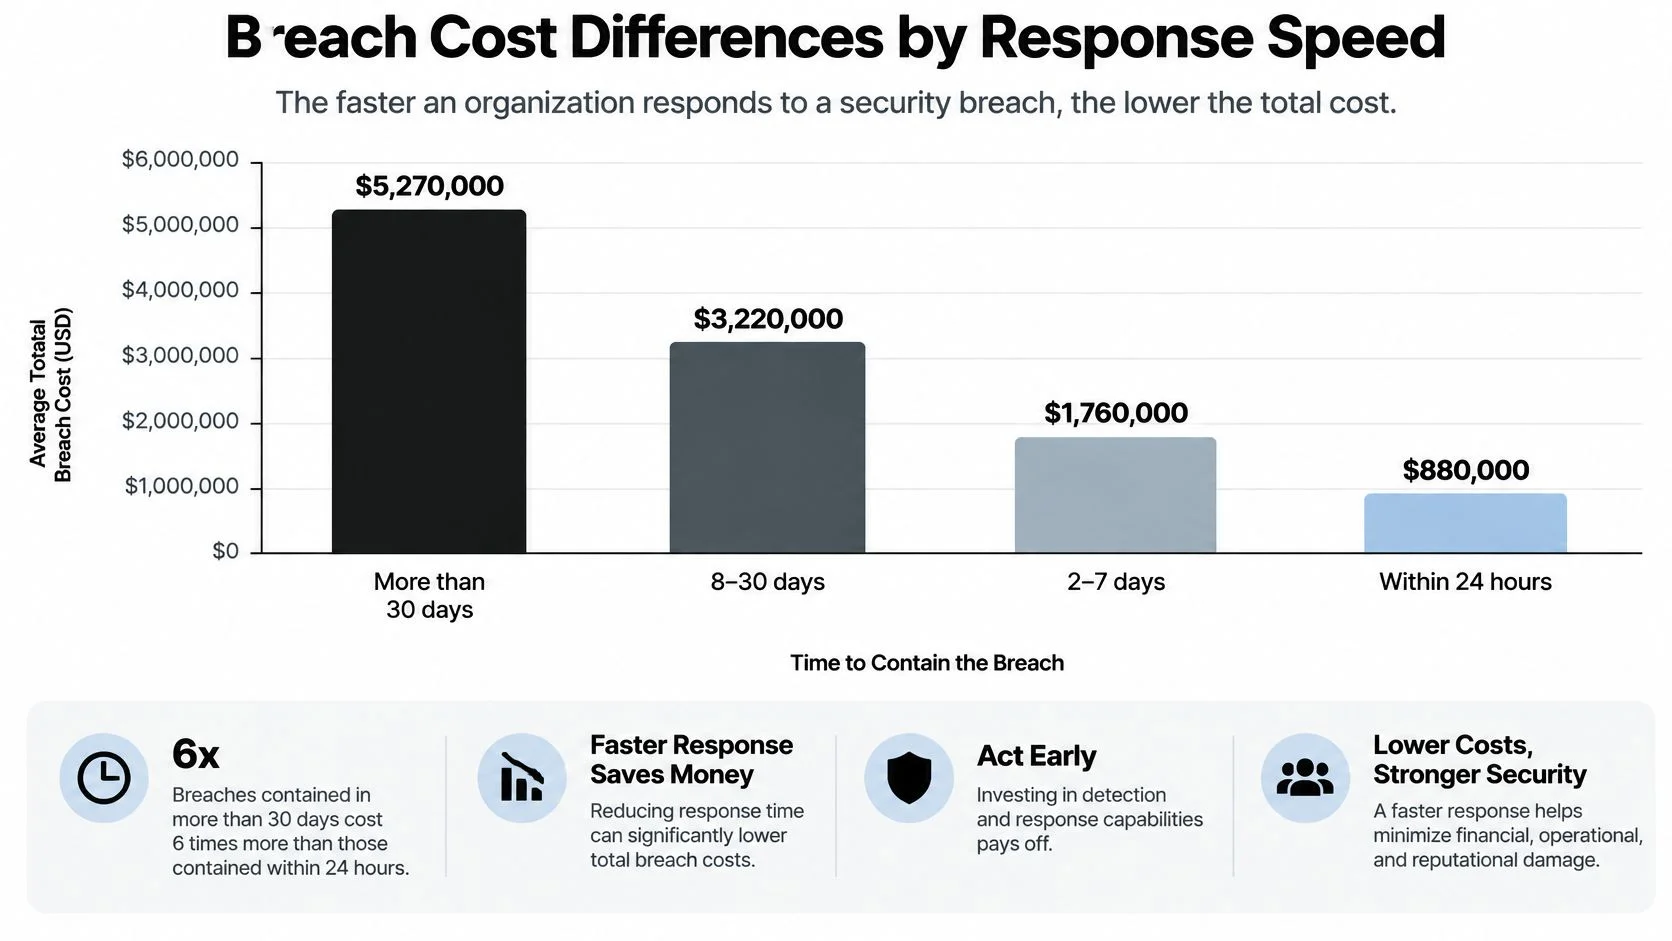
The comparison makes the financial relationship easier to see.
Turn benchmarks into working clocks
Don't accept the study's identification-and-containment average as a target. Your team needs shorter, action-specific service levels that it can test.
- Alert ownership: The on-call person acknowledges the alert and hands it to a named investigator, rather than leaving it in a shared inbox.
- Credential containment: IT disables confirmed stolen credentials immediately under pre-approved authority, with an exception route for safety-critical services.
- System isolation: The technical lead chooses targeted isolation where possible and records any business interruption.
- Executive updates: The incident lead sets the next briefing time even when the investigation remains incomplete.
Automation can revoke sessions or quarantine a device quickly, but a mistaken rule can also interrupt legitimate work. Test narrow actions first, keep an audit trail, and identify who can reverse them.
Budget for response, not just reimbursement
Insurance and operational readiness solve different problems. Reviewing what data breach coverage includes can help you identify questions about approved forensic providers, notice expenses, and claim conditions.
Pick an internal identify-and-contain target far inside the shorter lifecycle benchmark, then write it beside the detection and containment owners. For active account compromise, think in immediate response actions, not in months.
How to Assign Roles and Build the Playbook
Say a 12-person online shop is building its first playbook. The founder becomes incident lead, an IT contractor handles technical response, and retained counsel advises on privacy and notification decisions.
The role discussion should happen before an emergency, with responsibilities visible to everyone.
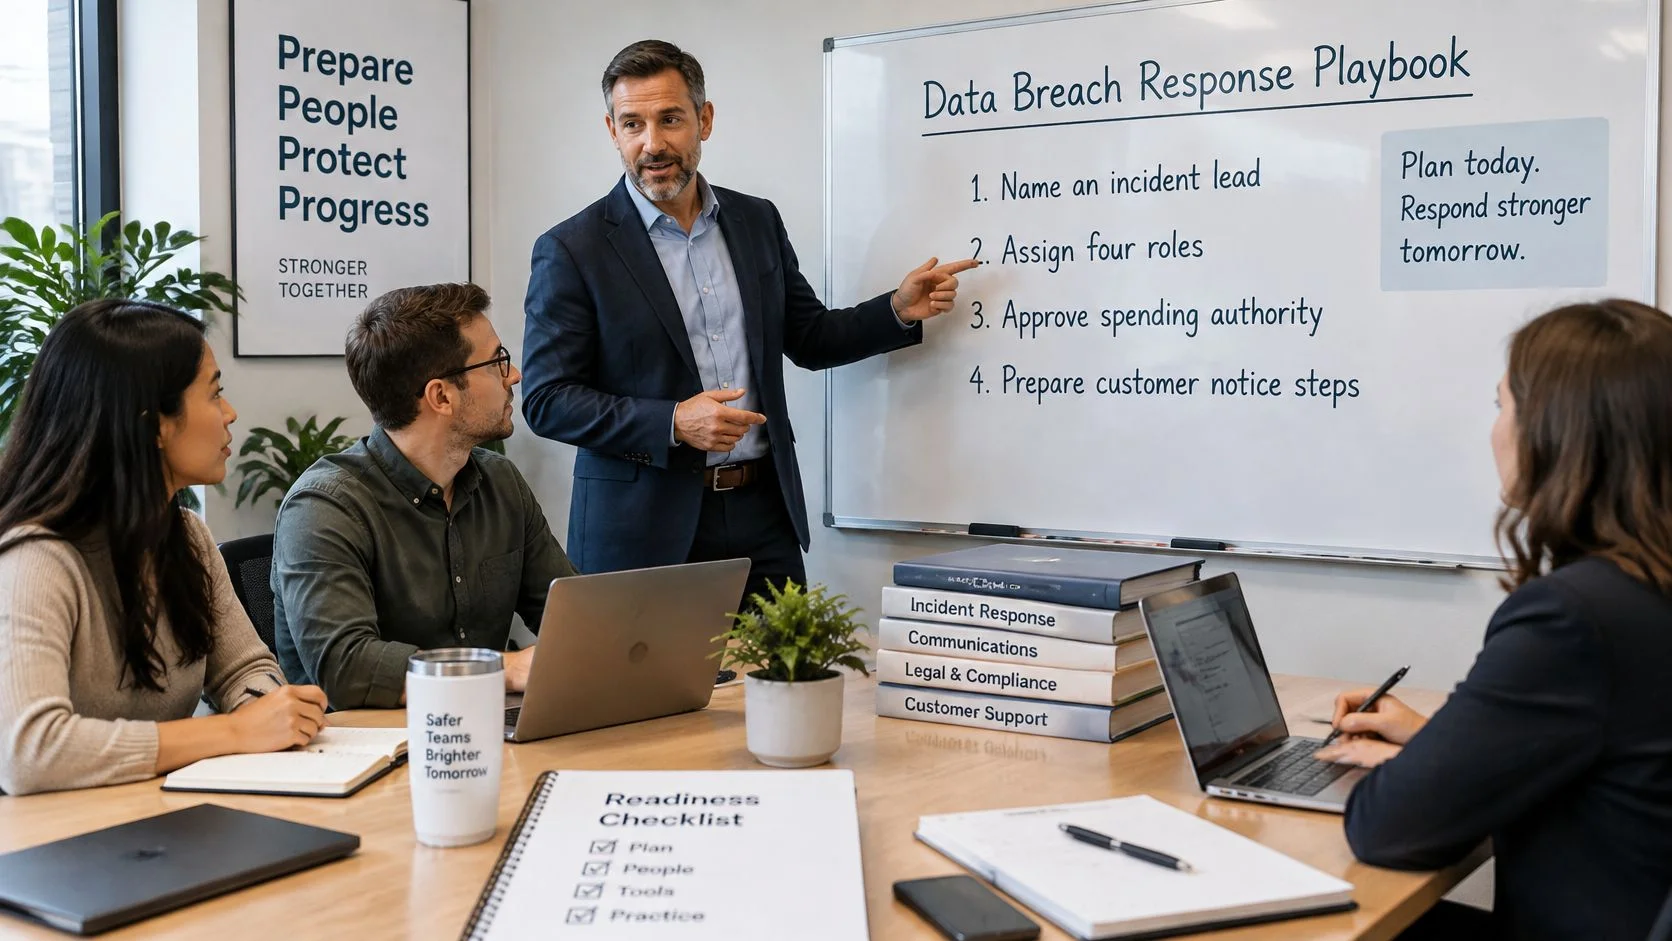
Build the operational pieces
-
Give the incident lead decision authority. Write down who can declare an incident, authorize forensic help, and approve customer-notice spending. Otherwise, responders may identify the right action but lack permission to take it.
-
Assign supporting seats and backups. Name owners for technical containment, legal and privacy, communications, and business recovery. In the shop scenario, an operations manager handles customer updates while the contractor investigates; the contractor shouldn't also be answering every customer email.
-
Make contact cards and test them twice a year. Include after-hours details for each owner, outside counsel, the insurer, important vendors, and the relevant regulator. Record how to reach the backup when the primary contact doesn't answer.
-
Map sensitive systems and approved restore sources. List where personal data, credentials, payroll, and customer records live. Include the backup location, its administrator, and the business owner who can confirm that restored information is usable.
-
Pre-approve safe initial actions. Specify when responders can disable an account, isolate a host, and preserve logs without convening a meeting. Require escalation before actions that could interrupt essential services.
-
Draft audience-specific holding statements. Prepare separate employee, customer, and partner messages stating confirmed facts, important unknowns, and the update location. Avoid promises that no data was taken until the evidence supports them.
-
Choose an independent response channel. Use a separately administered secure messaging service or phone bridge that doesn't rely on the suspected email environment. Test access from a clean device.
-
Rehearse a stolen-password scenario. Ask who notices an unfamiliar login, who revokes access, and who checks recovery settings. Record missing permissions and unanswered questions as assigned tasks.
Vendor responsibilities deserve particular attention. Review the data processing agreement alongside the playbook so contractual reporting routes match the contacts responders use.
Put timing beside authority
Write a clock beside alert ownership, credential disabling, host isolation, and executive briefing. Use immediate escalation for confirmed compromise and explicit handoff deadlines for investigation; don't let an industry average become an acceptable waiting period.
For the shop, the founder also names who can approve taking checkout offline if the contractor finds active theft. That trade-off belongs in the playbook because lost sales and continuing exposure both matter.
Use this video as a discussion aid during the team's rehearsal.
A missing owner is a plan gap, not a detail to settle during the breach.
How to Handle the First 72 Hours
The opening response window is for awareness, containment, and notification decisions. It isn't a promise that every application will be rebuilt before a reporting deadline.
Keep the priorities visible while technical and legal work proceed together.
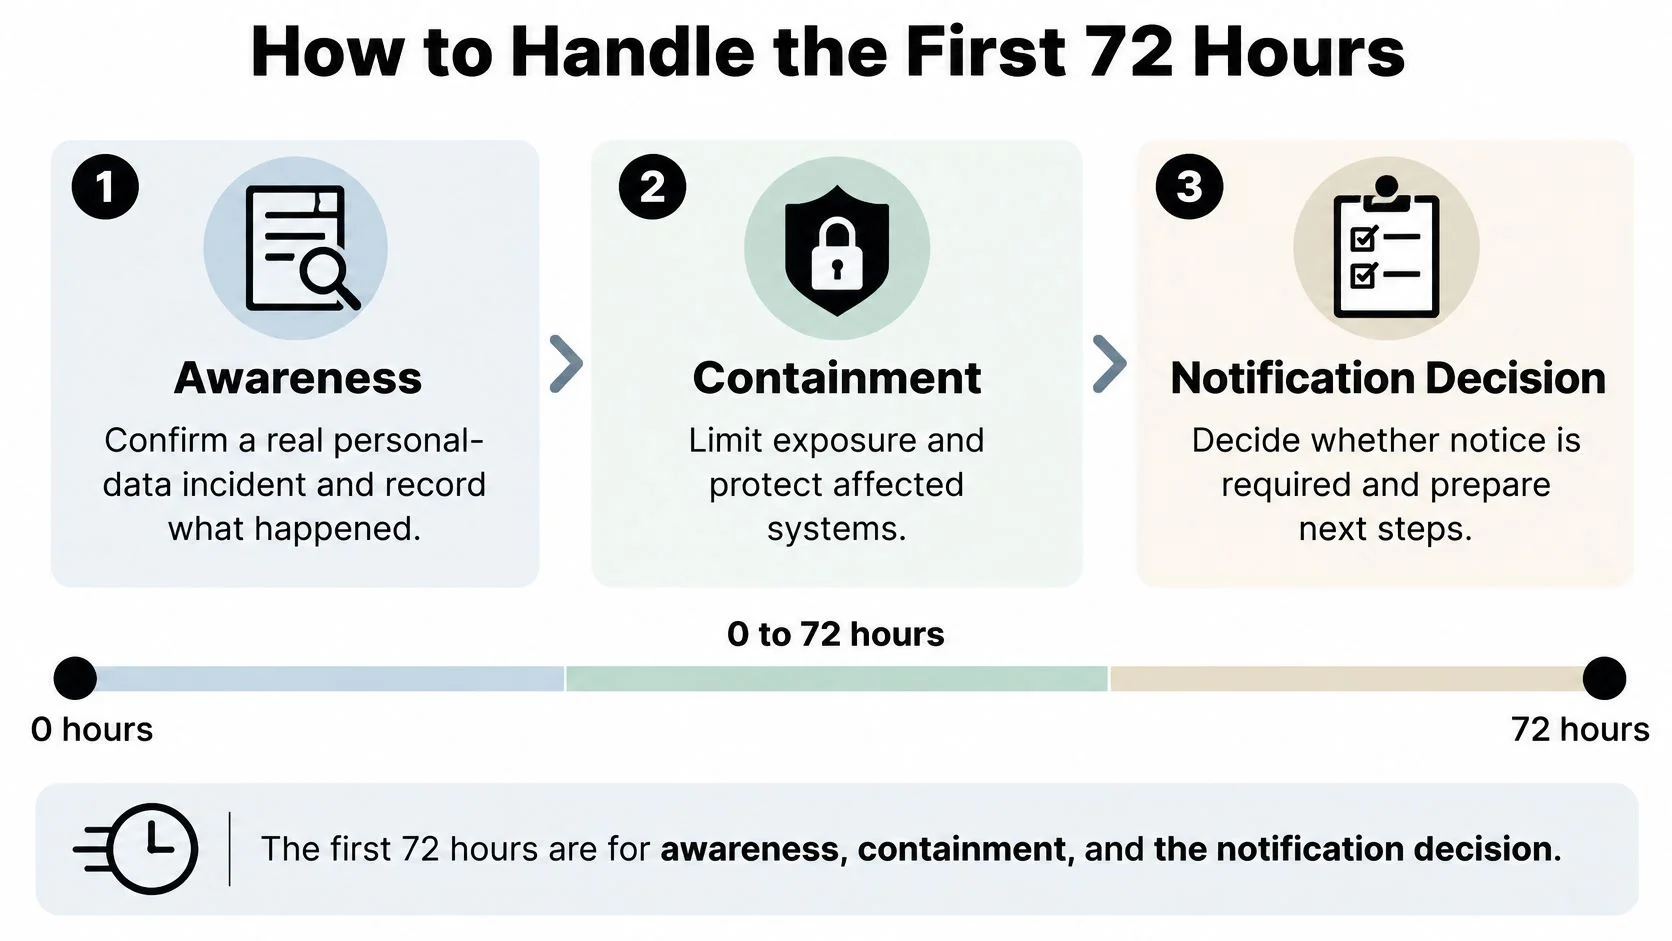
Establish facts without waiting for certainty
-
Record awareness. Confirm whether the event involves personal data and record when the organization became aware, who made that assessment, and the supporting facts. Don't confuse the attacker's entry date with the organization's awareness timestamp.
-
Protect evidence. Export relevant authentication, cloud audit, and application logs to restricted storage. Capture a system snapshot where appropriate before wiping or rebuilding, without delaying urgent action against ongoing harm.
-
Limit access. Isolate affected devices, revoke exposed tokens, and reset compromised passwords. A password reset alone may leave an existing session active.
-
Describe the scope. Record affected people, approximate record counts, data categories, and known access paths. Mark unknowns explicitly instead of entering reassuring guesses.
Make separate notification decisions
The EU controller and processor requirements below come from GDPR Article 33, which sets the authority-notification deadline at no later than 72 hours after awareness where feasible, unless risk is unlikely. The UK rules come from the ICO's personal-data breach guide, which requires notifiable breaches to be reported within 72 hours and high-risk breaches to be communicated to individuals without undue delay.
Notification clocks to decide within 72 hours
| Decision | Deadline | Who is told | Required substance |
|---|---|---|---|
| EU GDPR controller notice | Without undue delay and where feasible within 72 hours of awareness, unless risk is unlikely | Supervisory authority | Nature, categories and approximate counts, contact, consequences, measures; explain any delay |
| EU processor notice | Without undue delay | Controller | Facts the controller needs; phased detail is allowed |
| UK notice to the ICO | Without undue delay and no later than 72 hours after awareness | ICO, if the breach is notifiable | Notifiable personal-data breach after a documented risk assessment |
| UK notice to people | Without undue delay if high risk to rights and freedoms | Affected individuals | A separate decision from the ICO filing |
-
Have legal assess applicable duties. For EU reporting, prepare the available required information and provide further detail in phases when necessary. Missing facts aren't a reason to delay the decision.
-
Document the UK risk assessment. Consider the data type, likely consequences, and severity of harm. Record separate conclusions for the authority filing and direct communication to people.
-
Brief leadership. State what's confirmed, what remains unknown, what responders have done, and when the next update will arrive.
-
Start controlled recovery. Remove unauthorized access, repair the entry route, and restore from a trusted source. The business owner verifies the service before normal use resumes.
Keep a single incident status line: aware, contained, authority told, people told, service restored. Record “not required” with a reason rather than leaving a blank.
Give affected staff a practical guide to what to do after a data breach, while keeping organizational response decisions with the incident lead.
Notices That Tell People What to Do
Organizations providing root-cause details in public breach notices fell from 100% in 2020 to 30% in 2025, while notices withholding attack-vector details reached 70%, according to the Identity Theft Resource Center's 2025 Annual Data Breach Report. A recipient can't prioritize protection if the notice never distinguishes a leaked phone number from a stolen session token.
A timely message can still be practically useless. Someone managing payroll, a gaming account, and personal banking needs to know which actions come first.
Set a minimum information standard
Your notice template should identify the affected data categories, exposure dates, containment status, and whether authentication information was involved. Explain how the attacker entered and whether information was taken when those facts are established; otherwise, say they remain under investigation.
Maintain a living exposure inventory linking each breached identifier to affected systems and third parties. Update recipients when the confirmed scope changes, including when evidence narrows an earlier precautionary warning.
First action by what was exposed
| Exposed data | First action | Where the risk spreads |
|---|---|---|
| Passwords or session tokens | Reset the secret and revoke other sessions | Email, work, gaming, social, and finance logins that reused it |
| Government ID or similar documents | Place a credit freeze where available and start the replacement process with the issuer | New-account and impersonation fraud |
| Payroll or bank details | Call the institution and review recent transfers | Direct financial loss |
| Contact details only | Treat unexpected login or payment requests as phishing | Social engineering against the same person |
A credit freeze and document replacement depend on the country and document involved. Ask the issuing authority what protection or replacement is appropriate rather than assuming every exposed identifier can be changed.
Connect the notice to everyday accounts
Say an employee reused a work password on a gaming marketplace and a dating app. The notice should explain that changing the company password doesn't protect those other accounts, and that stolen tokens require session revocation rather than password changes alone.
For dating app verification or catfishing detection, independently confirm a contact through a trusted channel. Public profile matches can provide leads, but they don't establish identity or make a money request safe.
A compromised professional profile can also carry fraudulent messages to recruiters or colleagues. Preserve evidence, recover the account, and correct impersonation clearly without republishing sensitive details.
Use your data breach notification requirements checklist to check legal completeness, then test whether a recipient could act without calling support.
If the notice doesn't say what was exposed, the plan treats the wider identity as exposed until proven otherwise. That's a precaution for protective action, not a claim that every account was breached.
Keep the Plan Ready and Check Leftover Exposure
A plan stays useful when someone maintains it between incidents. Give recurring tasks to named owners and put them on the calendar, rather than relying on everyone to remember.
Maintain a small, testable routine
- Incident lead, twice a year: Run a 45-minute tabletop and test the contact list. Repeat the exercise after a major system or vendor change, and replace any contact route that fails.
- Incident lead, after a real incident: Within ten business days, record the cause, cost, and a concrete control change. If investigation remains open, document provisional findings and assign a follow-up date.
- IT and HR, when access changes: Update the exposure inventory when people join or leave. Provide a voluntary way for employees to flag work identifiers used elsewhere without asking for personal passwords.
- Legal and insurance owner, annually: Review notice clauses, approved response providers, and spending approval routes. Don't assume an old policy attachment still matches the active contract.
- Plan custodian, after every revision: Date the cover page and confirm that owners can reach the current version outside the company email environment.
These are practical operating cadences, not universal legal deadlines. A small team can adjust the schedule, but every task still needs an owner and a completion record.
Store the plan, contact cards, and emergency administrator access outside the potentially breached email tenant. Keep emergency credentials in a controlled password vault, protect them with strong authentication, and test the recovery route without exposing secrets during the exercise.
Watch for misuse after technical recovery
Once services are stable, assign customer support or security an owner for reports of lookalike login pages and urgent payment messages. Give people a known support route so they don't have to trust links in a new warning email.
For individuals, prioritize unique passwords and multifactor authentication on email and other high-impact accounts. A password manager such as Bitwarden or 1Password can help replace reused credentials; an authenticator app or security key can strengthen sign-in where supported.
Romance scams and account-recovery scams may use genuine leaked details to sound credible. If a supposed partner asks for money, independently verify the person, preserve messages and payment records, and contact the financial institution promptly if you've paid.
Ongoing data breach monitoring can support follow-up, but a clean result doesn't prove that information was never exposed. Monitor account-provider alerts and financial activity as well.
Run a scenario this week
Choose a leaked customer spreadsheet or a stolen administrator password. Ask participants to produce the awareness timestamp, containment owner, authority-notification decision, and a plain sentence naming the exposed data.
Then introduce a complication: the administrator's recovery email is also compromised, or the spreadsheet contains payroll details rather than contact information. Check whether the team changes its actions and message appropriately.
Pass the exercise only when someone can carry out each action with available access. Fix that page before adding more policy.
For residual exposure, Digital Footprint Check is one OSINT option alongside account-provider security dashboards and password-manager checks; it searches 500-plus platforms, including social networks, breach data, gaming profiles, professional sites, and public records. Use the free footprint checker with an email you own or are authorized to assess, then investigate exposed identifiers and replace any credential confirmed as leaked or reused.
Keep identity checks proportionate. Parents, employers, and people checking dating profiles should respect consent, privacy, and applicable screening rules; a matching username isn't proof that accounts belong to the same person.
A restored server with untouched, at-risk personal accounts is an unfinished incident.
Digital Footprint Check helps you discover exposed personal information and accounts that may need attention after a breach. Visit Digital Footprint Check to review your online footprint and turn relevant findings into account-recovery and identity-protection actions.