· Digital Footprint Check · Content Marketing · 13 min read
How Can I Secure My Phone From Hackers in 2026
How Can I Secure My Phone From Hackers. Learn how to secure your phone from hackers with proven steps on updates, authentication, app safety, VPNs
You're stepping out of a rideshare when you realize your phone is still on the seat. By the time you reach the car, it's gone. The immediate panic isn't just about replacing the device. You're thinking about your bank app, work email, password manager, authenticator codes, photos, payment cards, and every account that uses your phone number for recovery.
That reaction is rational. A modern phone is part computer, part identity vault, and part keyring for your digital life. How can I secure my phone from hackers? Not with one magic setting. You need layered protection that makes the device difficult to access, the accounts difficult to take over, and the stored data difficult to exploit.
Why Phone Security Feels Urgent Right Now
A stranger holding your phone can do more than read messages. They may reach email accounts, reset passwords, approve sign-ins, access work systems, or use stored payment methods. Even a locked phone remains valuable if an attacker can move your number to another SIM, trick you into surrendering a code, or sign in through credentials that leaked elsewhere.
Attackers increasingly combine technical access with social engineering. Fake banking apps, delivery messages, toll notices, urgent account alerts, and convincing calls all aim to make you perform the dangerous action yourself. Verizon's 2026 Data Breach Investigations Report announcement says interactive mobile-centric attacks, including fake text messages and voice calls, have a success rate 40% higher than traditional email phishing.
Kaspersky's 2025 mobile threat report recorded approximately 1.17 million attacks per month against mobile devices and 14,059,465 mobile attacks blocked during the year. Adware represented 62% of detections, while researchers identified more than 815,000 malicious installation packages, including 255,000 mobile banking Trojans. The practical lesson is simple: mobile threats aren't confined to one malware family or one country.
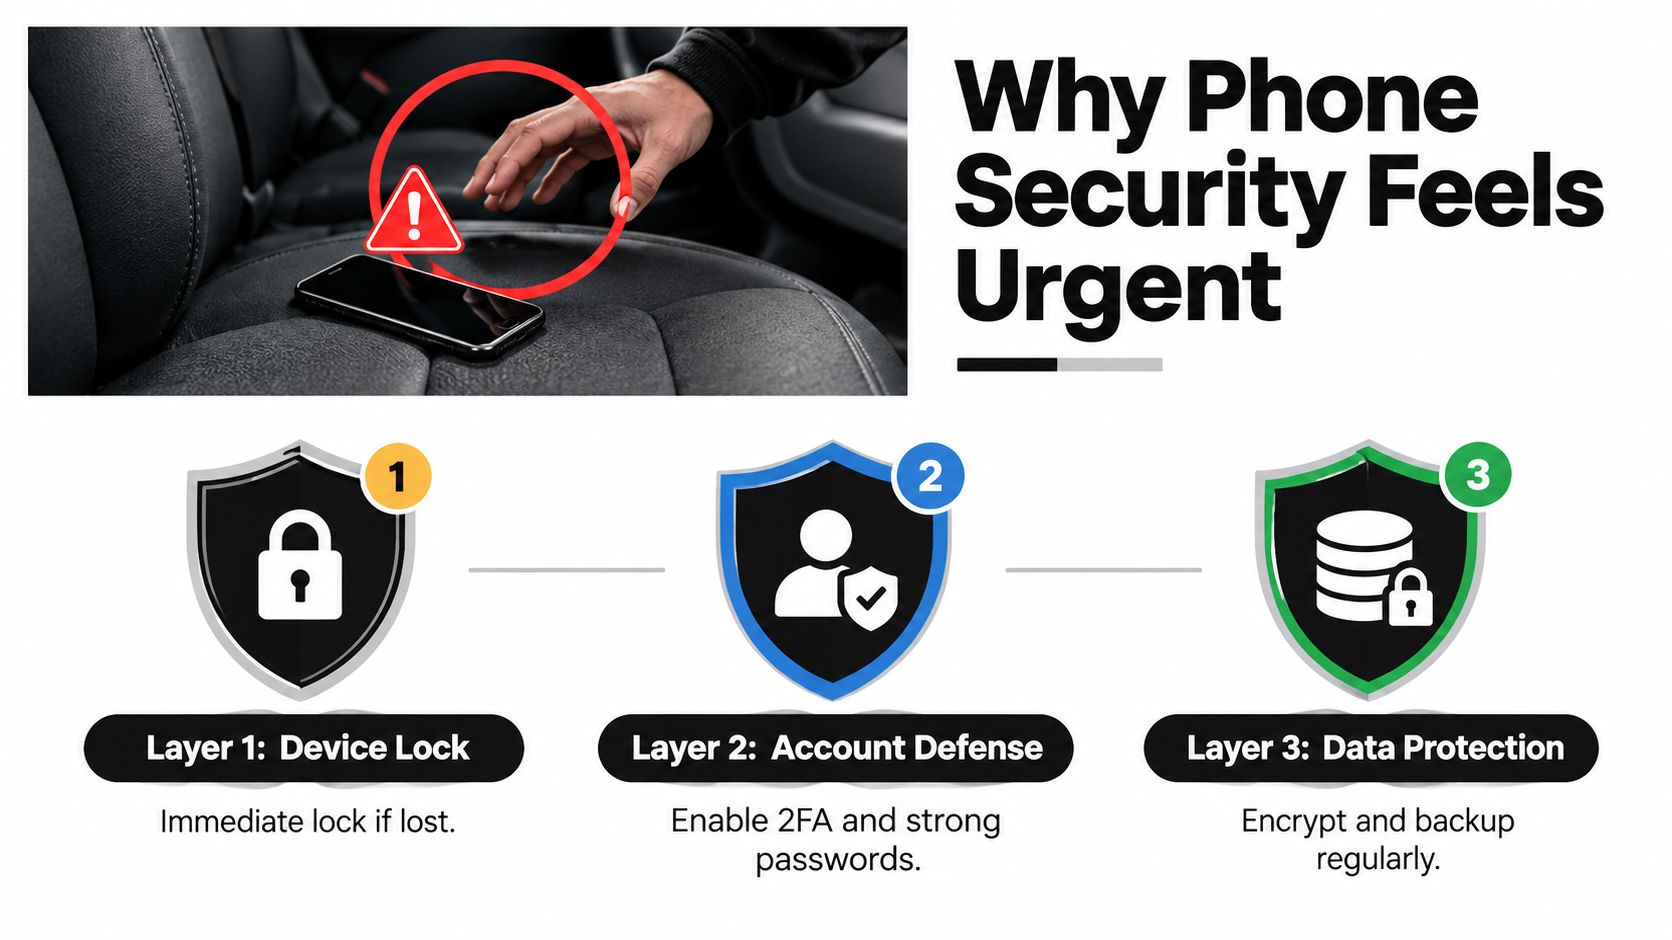
Think in layers, not gadgets
The first layer is the physical device. A strong screen lock, biometric authentication, automatic updates, and short auto-lock time reduce the damage from loss or theft. The second is account defense, including unique passwords, authenticator apps, passkeys, security keys, and carrier protections. The third is data protection, including encrypted backups, remote location tools, and a tested recovery process.
No single setting blocks every path. A passcode can't stop a convincing phishing page, and an authenticator app can't help if someone has already taken over your email recovery account. Your objective is to remove easy opportunities until a thief or scammer decides you aren't worth the effort.
Lock the Door With Updates, PINs, and Two-Factor Authentication
A stolen phone with an outdated system, a weak PIN, and SMS-only account protection gives an attacker several easy openings. Close those openings in order, starting with updates.
On iPhone, open Settings > General > Software Update > Automatic Updates. On Android, check Settings > System > Software update, though menu names vary by manufacturer. Update apps through the App Store or Google Play, and keep automatic app updates enabled where available.
Security patches matter because attackers target flaws developers have already fixed. Delaying an update leaves a known weakness available and usually requires little effort to exploit.
Set a strong screen lock next. On iPhone, go to Settings > Face ID & Passcode or Settings > Touch ID & Passcode. On Android, use Settings > Security and privacy > Device access, or the equivalent menu on your phone. A six-digit PIN is a sensible minimum. Choose a longer alphanumeric password if theft, travel, public demonstrations, or shoulder surfing are realistic risks.
Biometrics make daily access easier, but the underlying passcode still protects the device after a restart or when biometric authentication is unavailable. Set auto-lock to a short interval, and hide lock-screen previews for sensitive messages.
Protect the number behind the phone
Set a SIM PIN through your cellular or mobile network settings. It will not block every carrier-account attack, but it adds protection if someone removes the SIM. Contact your carrier too, then establish an account PIN or port-out restriction.
SMS authentication is better than no second factor, but SIM swaps and number-port abuse can defeat it. Use an authenticator app, passkey, or hardware security key for email, banking, cloud storage, and primary social accounts. Store recovery codes offline or in a secure password manager that does not depend on the missing phone.
If you need to test SMS workflows without exposing your primary number, you can rent a temporary number. Do not use temporary numbers as permanent recovery credentials.
Use this personal cybersecurity best practices guide to review the wider account and device setup, not just the phone settings.
Where Modern Phone Attacks Actually Land in 2026
The most dangerous attack may not look like malware. It may arrive as a text message claiming that a delivery failed, a toll payment is overdue, or a bank account needs verification. The link opens a page that copies a familiar login screen, captures your password, and may immediately request a one-time code.
Lookout reported more than 1,000,000 mobile phishing and social-engineering attacks against enterprise users in Q1 2025, along with 193,000 malicious or vulnerable apps on enterprise devices. Its reporting also recorded 10,546,471 phishing, malicious, denylisted, and offensive websites blocked in that quarter. Those figures reinforce why phone security has to include browsing and messaging behavior, not just antivirus scanning.
Zimperium reported that smishing represented over two-thirds of mobile phishing attacks, while vishing and smishing rose 28% and 22%, respectively, in its mobile attack research. Kaspersky also described a VPN app that intercepted login codes sent through text messages. A user can therefore install an app that appears protective while handing an attacker access to authentication traffic.
| Attack Vector | How It Reaches the Phone | Typical Damage |
|---|---|---|
| Smishing | A text leads to a fake bank, delivery, toll, or account page | Stolen passwords, payment details, or one-time codes |
| Vishing | A caller creates urgency and asks for a code or account action | Account takeover or disclosure of recovery information |
| SIM swapping | A carrier transfers your number to an attacker-controlled SIM | Intercepted SMS codes and disrupted phone service |
| Credential stuffing | An attacker tests leaked email and password combinations | Cloud, social, gaming, or financial account access |
| Recovery fraud | A scammer persuades support staff to reset an account | Loss of control even when the phone itself remains intact |
The common thread is identity control. An attacker may never install a traditional virus. They can instead take over the number, cloud account, email inbox, or recovery process that governs the phone's most important services.
If you see unknown apps, strange account activity, unexpected codes, or unusual behavior, use a structured guide on how to find spyware on your phone, then secure your accounts from a separate trusted device.
Apps, Permissions, and Networks You Can Control
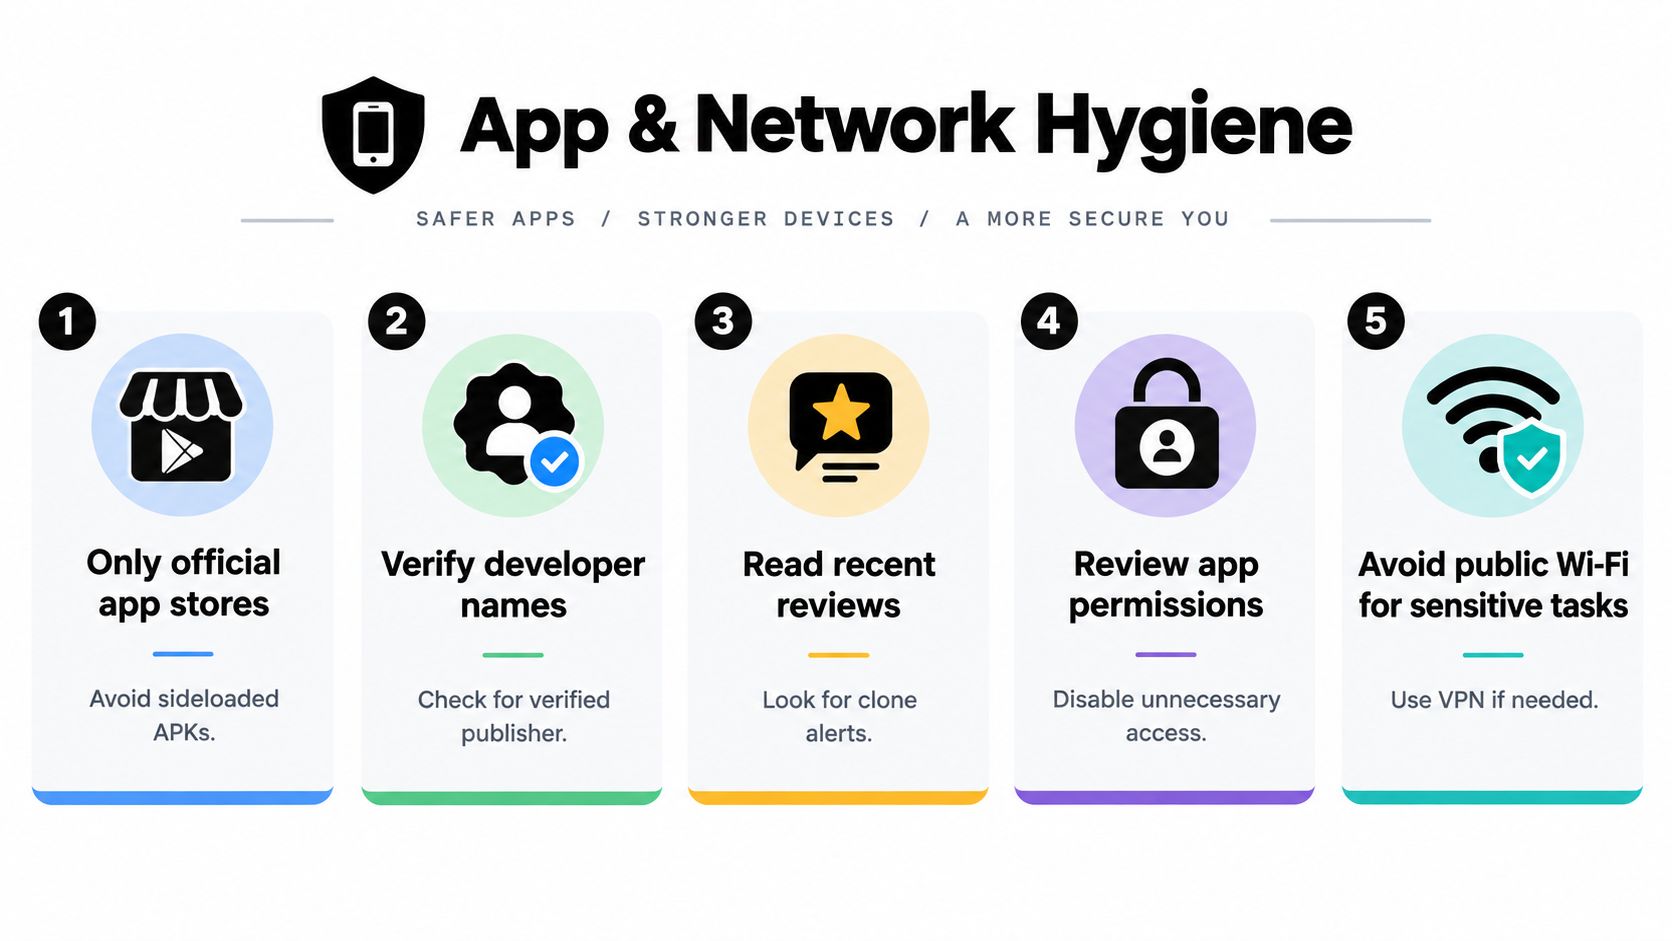
App discipline starts before installation. Use the Apple App Store or Google Play, check the developer name, inspect recent reviews, and look for warnings about cloned apps. Avoid sideloaded APKs unless you understand exactly who built the package and why you need it. A familiar logo doesn't prove an app is genuine.
Free utilities deserve extra suspicion when they request access to contacts, messages, microphones, accessibility controls, or notification content. A flashlight app doesn't need your contacts. A wallpaper app doesn't need your microphone. A VPN that demands broad access while offering no clear privacy explanation is a poor trade.
Reduce permissions to the minimum
On iPhone, review Settings > Privacy & Security. On Android, use Settings > Security and privacy > Privacy > Permission manager, or search Settings for “permissions.” Check location, camera, microphone, contacts, photos, Bluetooth, and background activity one app at a time.
Choose Never, Ask next time, or Only while using the app where the function doesn't require constant access. Remove unused apps instead of merely disabling notifications. Dormant software can retain permissions and may become risky after an update or account change.
A reputable mobile security tool can add on-device scanning, especially on Android. Treat excessive permission requests as a warning sign, even when the product markets itself as security software. A scanner that needs access unrelated to scanning creates another privacy problem.
For a broader app review, consult these mobile app security best practices for 2025.
Treat networks as exposed spaces
Disable auto-join for open Wi-Fi and forget networks you no longer use. Don't perform banking or account recovery on an unknown hotspot. If public Wi-Fi is unavoidable, use a reputable VPN and confirm that you're visiting the correct site before entering credentials.
CISA's consumer mobile device cybersecurity checklist also recommends disabling unneeded radios such as Bluetooth, NFC, Wi-Fi, and GPS. It warns that malicious chargers or connected computers can load malware that bypasses protections, so use your own charger and avoid unknown USB ports when handling sensitive accounts.
Reviewing permissions regularly is easier with a written routine. This app permission management guide can help you turn that routine into a repeatable privacy check.
Backups, Find My, and What to Do If Your Phone Goes Missing
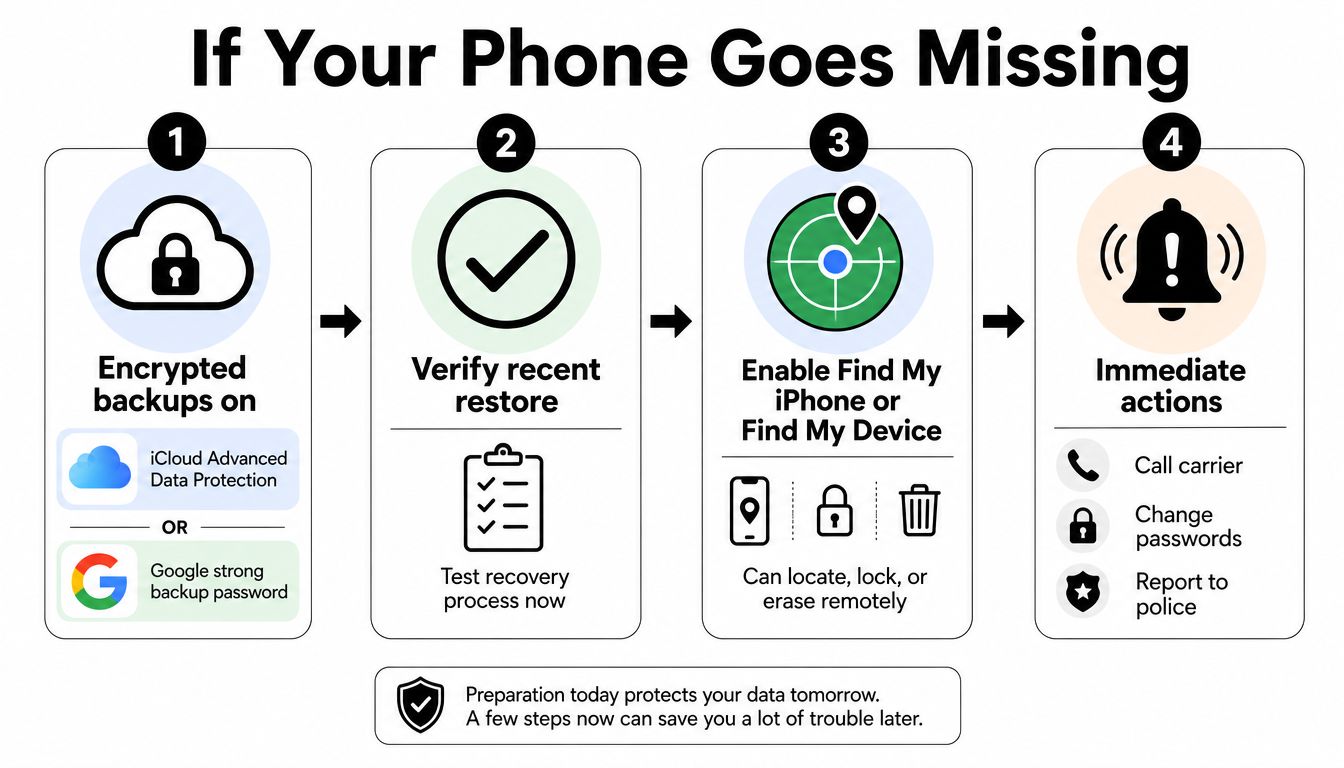
A secure phone still needs a recovery plan. Without an encrypted, current backup, you may delay remote wiping because you're afraid of losing irreplaceable photos, messages, contacts, or work files. That hesitation gives whoever has the phone more time.
On iPhone, enable iCloud Backup and consider Advanced Data Protection if it fits your recovery capabilities. On Android, enable Google backup and protect the account with a strong unique password and a secure second factor. Don't assume a backup works because the setting says “on.” Verify that important data restores successfully to a trusted device or through the platform's available recovery process.
Prepare location and remote controls early
Enable Find My iPhone before the phone disappears. On Android, enable Find My Device. Confirm that location services and the relevant cloud account are active, then learn where the remote lock, contact-message, and erase controls are located. You don't want to discover the process while standing outside a police station.
If your platform supports sharing a low-battery location with a trusted contact, enable it only for someone you trust. Keep a current contact number available for the lock screen, but don't display an email address, home address, or other personal detail.
If the phone vanishes, act in this order:
- Lock it remotely: Use Find My iPhone or Find My Device and display a short contact message.
- Call your carrier: Suspend the line, set or change the port-out PIN, and request a SIM-transfer freeze.
- Protect money: Revoke payment cards linked to the device and suspend mobile wallets.
- End cloud sessions: Force logout from email, cloud storage, social media, work systems, and password managers.
- Change priority passwords: Start with email, carrier access, banking, and the account controlling device backups.
- Erase as a last resort: Wipe the device once you've confirmed that essential data is recoverable.
If account access looks suspicious even after you recover the device, use this guide on how to get rid of hackers for containment steps.
Watch Your Credentials and Your Wider Digital Footprint
A locked phone can't protect an account whose password already sits in a criminal database. Credentials leak through breached services, reused passwords, old accounts, exposed email addresses, and information gathered by data brokers. Attackers then test those combinations against email, banking, gaming, shopping, and workplace services.
Start with Have I Been Pwned or the exposure tools built into a reputable password manager. Check whether your email addresses appear in known breaches, then act on every result. Change reused passwords across all affected services, not just the service named in the breach. Use a password manager to create unique credentials, because memorizing one password for every account encourages exactly the reuse attackers exploit.
Read warning signals as incidents
| Warning Signal | Immediate Response |
|---|---|
| An unexpected password-reset email | Don't click its links. Open the service directly, review sessions, and change the password if necessary |
| A one-time code you didn't request | Treat it as an attempted sign-in. Check account activity and contact support through the official channel |
| Sudden loss of mobile service | Call the carrier from another phone and ask whether a SIM or number transfer occurred |
| A login alert from an unfamiliar device | End the session, rotate the password, and replace SMS authentication |
| Friends receive strange messages from you | Warn contacts, inspect messaging apps, and review connected sessions |
| An old breach appears in a new alert | Change any still-reused password and remove outdated recovery details |
Social engineering often turns small pieces of exposed information into a convincing story. A public phone number, employer, username, pet name, or account-history detail can help a caller sound legitimate. Your digital footprint therefore affects the security of your phone even when the device itself has never been infected.
Phishing-resistant authentication deserves priority. CISA's mobile communications best practices prioritize end-to-end encrypted communications and FIDO authentication for higher-risk users. SMS-based MFA remains vulnerable to SIM-swapping and number-port abuse, while FIDO keys and passkeys bind authentication more closely to the legitimate service and device.
For people who want ongoing exposure checks rather than a one-time breach search, Digital Footprint Check can scan publicly accessible information across email, phone numbers, usernames, social profiles, breach databases, gaming profiles, professional networks, and public records. Use this guide to identify a cloned SIM card if your phone suddenly loses service or your carrier reports an unexpected transfer.
A Simple Phone Security Checklist You Will Actually Use
A complicated security ritual isn't necessary. A short list that protects the accounts and attack paths used every day is what's needed.
Complete these controls first
- Install current OS and app updates. Turn on automatic updates and don't postpone security prompts.
- Use a six-digit PIN or stronger passcode. Add Face ID, Touch ID, or Android biometrics for convenience, but keep the underlying code private.
- Protect email and banking with strong MFA. Prefer a passkey, authenticator app, or hardware security key. Treat SMS as a fallback, not your ideal.
- Use a reputable VPN on public Wi-Fi. Better still, use cellular data for sensitive activity on an unfamiliar network.
- Audit app permissions. Revoke camera, microphone, location, contacts, and background access when an app doesn't need them.
- Enable encrypted backups and test recovery. A backup that has never been restored is an assumption, not a plan.
- Enable Find My iPhone or Find My Device. Confirm that you can remotely lock the phone and understand when to erase it.
Keep the routine lightweight
Run a Digital Footprint Check scan monthly for exposed credentials and personal information. Review carrier protections quarterly, including the account PIN, port-out controls, and SIM-transfer settings. Check active sessions after every suspicious message, unexpected code, or loss of mobile service.
Skip low-yield theater. Third-party lock screens add friction without replacing the operating system's security model, and antivirus on iPhones usually isn't the answer to phishing, SIM swapping, or stolen credentials. The phone is one node in your identity system, not an isolated gadget.
Practical rule: Revisit your setup after international travel, starting a new job, taking control of sensitive accounts, or receiving a message that feels unusually urgent.
The point of phone security is not to make your device impossible to attack. It's to prevent a lost phone from becoming an identity takeover, stop a fake message from becoming a stolen password, and make account recovery difficult for anyone who isn't you.
Digital Footprint Check helps you find exposed personal information, leaked credentials, phone-linked records, and hidden online profiles that can make phone attacks easier. Run a free check today, then visit Digital Footprint Check to see what your wider digital footprint reveals and decide which exposures need attention.