· Digital Footprint Check · Content Marketing · 16 min read
Risk of Identity Theft: What It Is and How to Stay Safe
Learn the real risk of identity theft, common attack methods, and practical steps to monitor your exposure and protect your personal data online.
In 2025, the Federal Trade Commission received 1,358,253 identity theft complaints, up from 1,135,265 in 2024, according to Experian's summary of FTC identity theft statistics. That figure counts complaints, not every person affected, and it shows why the risk of identity theft deserves more attention than occasional credit-card monitoring.
Identity theft now reaches far beyond a stolen card number. A criminal might take over an email inbox, impersonate you on social media, hijack a gaming profile, or create a dating-app account that uses your name and photos. The damage can involve money, access, employment opportunities, personal safety, and reputation.
The most useful starting point is an OSINT-driven self-audit. Before you can protect an exposed email address, username, phone number, or old account, you need to know where that information appears and which accounts still depend on it.
What Identity Theft Actually Means in 2026
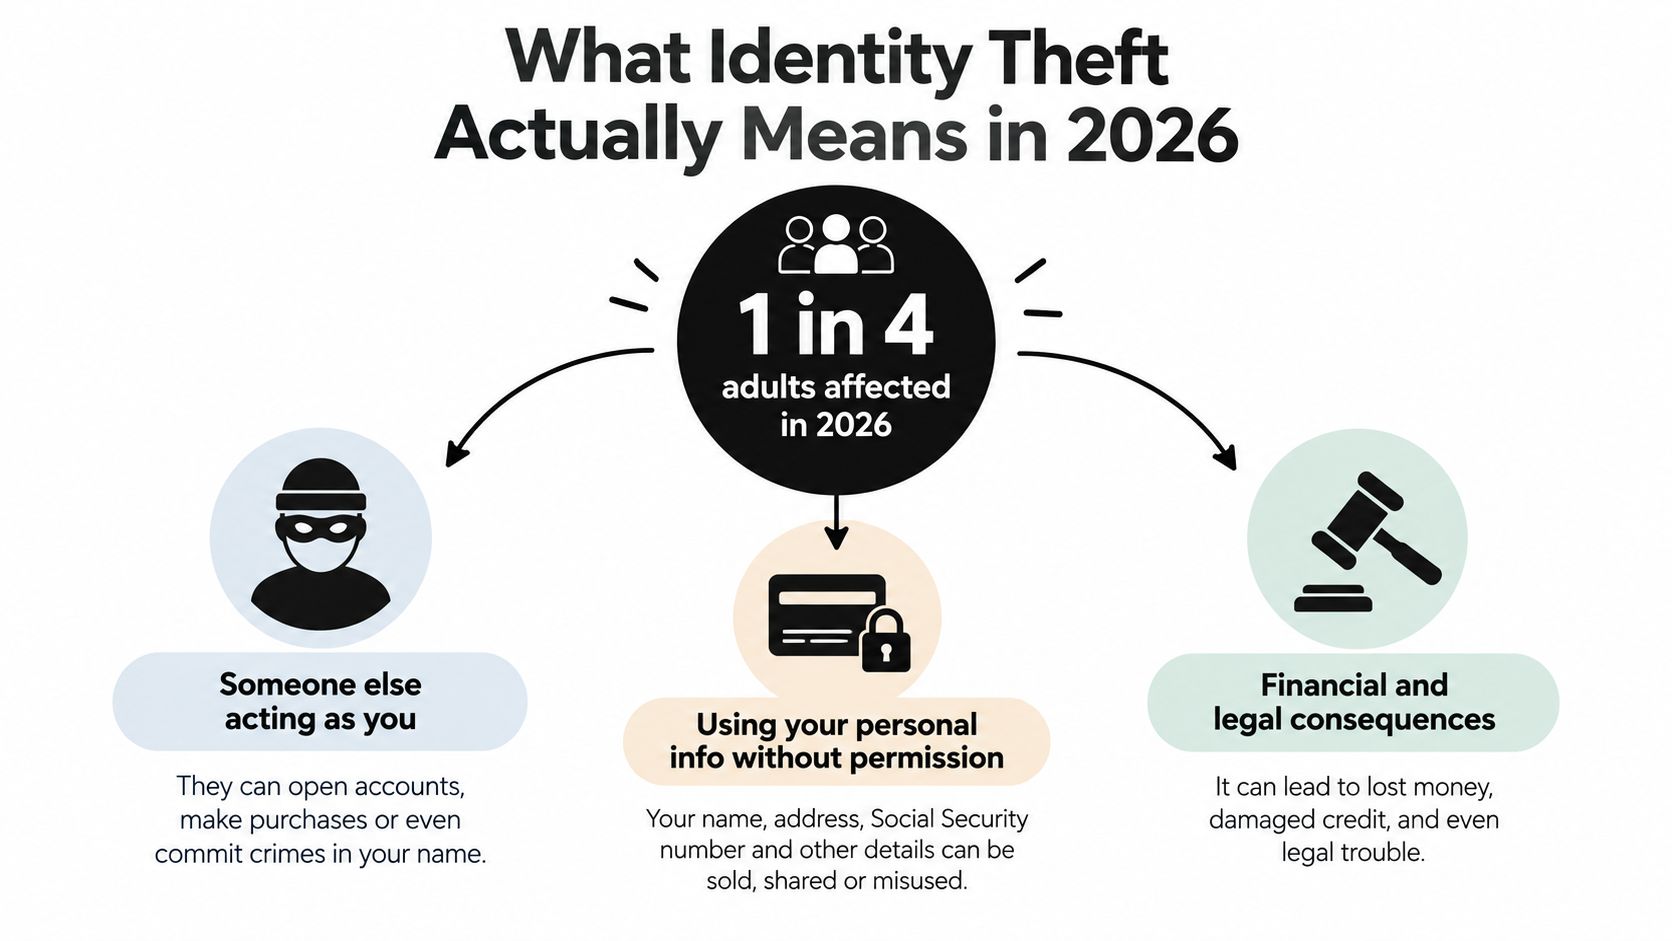
Identity theft means someone else uses your personal information to act as if they were you. The information might help a criminal open an account, reset a password, impersonate you in a message, or enter a service that belongs to you.
A simple analogy helps. Your accounts are rooms in a house, and your email address, passwords, phone number, and recovery details are keys. If a stranger gets a copy of one key, they may try it on several doors. If the same key works everywhere, a small exposure can become a much larger intrusion.
The FTC complaint total shows the scale of the traditional problem, while newer forms of misuse expand the consequences. The 2025 Consumer Impact Report from the Identity Theft Resource Center found that social media account takeover had become the most commonly reported form of identity misuse for the general population. That means a person can suffer identity harm even when no bank account is emptied.
Plain-language rule: If another person can use your information, profile, or account to convincingly represent themselves as you, treat it as an identity risk.
Four terms worth knowing
- Personally identifiable information, or PII: Details that can identify or help identify you, such as your name, address, phone number, email address, date of birth, or government identification number.
- Account takeover: A criminal gains control of an existing account, often by stealing credentials or defeating recovery controls.
- Synthetic identity: A fabricated identity assembled from real and invented information, which may be used to obtain services or accounts.
- Identity misuse: Someone uses your personal details, profile, image, or account access without permission, even when the immediate goal isn't direct financial theft.
The rest of this guide helps you recognize common entry points, understand the scale of exposure, follow a realistic consequence chain, assess your own situation, and build layered defenses. The aim isn't perfect certainty. It's to identify the next action that makes your exposed information less useful.
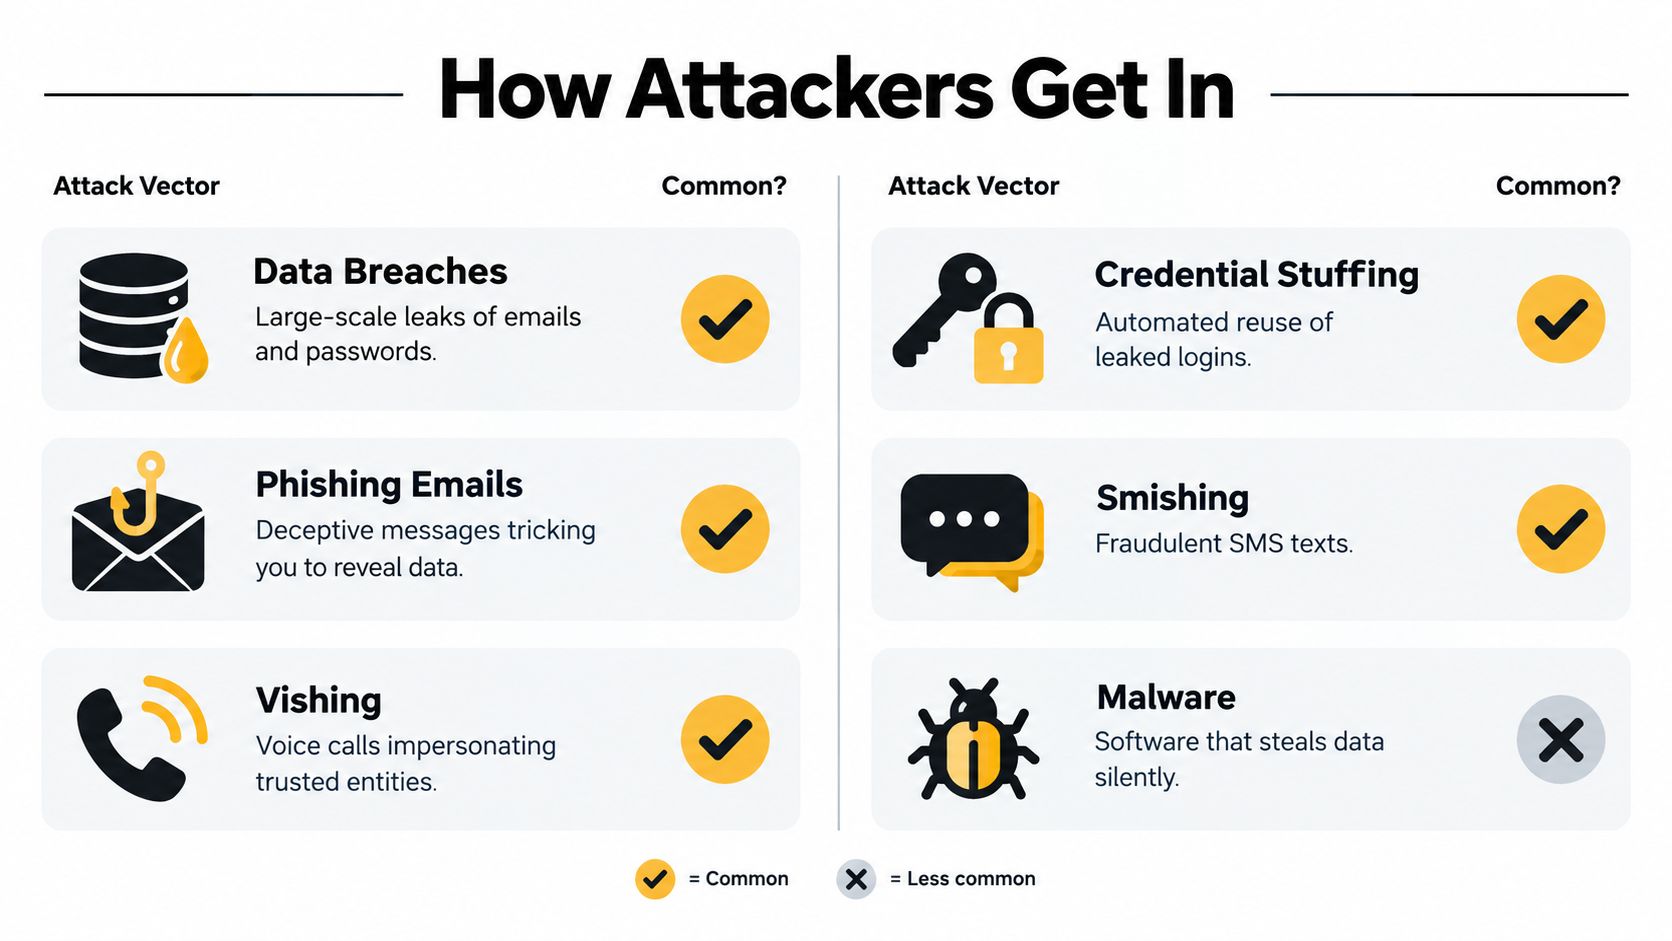
How Attackers Get In - Common Vectors to Recognize
Attackers rarely need one dramatic breakthrough. They usually collect small pieces from different places and connect them.
Six recognizable entry points
-
Data breaches expose emails, passwords, tokens, and other account information. You might receive a breach notice for an old forum account that you no longer remember using.
-
Credential stuffing uses automated tools to test leaked usernames and passwords on other services. The familiar scene is an old password opening a shopping, gaming, or social account because it was reused.
-
Phishing emails imitate banks, employers, streaming services, or tax agencies. A message may claim that your account will close unless you sign in through a lookalike page.
-
Smishing texts deliver the same deception by phone. A fake courier message may resemble a real tracking notification and direct you to a page that requests payment or login details.
-
Vishing calls use voice and urgency. Someone claiming to represent your bank may ask you to “confirm” a one-time code, even though that code is authorizing access.
-
Malware steals information after a person installs a malicious app, attachment, browser extension, or unofficial game modification. The software may look useful while collecting credentials.
Public Wi-Fi can also create exposure when people connect to an untrusted network and enter sensitive information without adequate device protection. Social profiles create a different problem. Public birthdays, family names, locations, workplaces, pet names, and travel routines can help attackers answer security questions or write believable messages.
Physical theft still matters. A lost wallet, stolen mail, discarded document, or unattended phone can provide details that digital criminals combine with information found online.
The Cybersecurity and Infrastructure Security Agency's guidance on compromised credentials emphasizes that stolen usernames, emails, passwords, and tokens can support credential attacks, phishing, lateral access, and resale. Password reuse is especially dangerous. The risk analysis cited in the verified data found 60% password reuse among users exposed in multiple breaches, rising to 87% among .gov employees (Sentilink's credential-exposure analysis).
Attackers often chain these vectors. A breach supplies a password, a public profile supplies a family detail, and a phishing text supplies the final opening. If your phone number may be exposed or targeted, review the practical warning signs in this guide to clone SIM cards.
This short video offers another visual explanation of common attack paths:
The Scale of the Risk in Numbers
The Identity Theft Resource Center recorded a record 3,322 data compromises in 2025, a 79% increase over five years. At the same time, the number of people affected fell from 1.36 billion in 2024 to 278.8 million in 2025. The center attributed that change to attackers targeting fewer people more precisely (the ITRC 2025 Annual Data Breach Report).
That combination changes how the risk should be read. More compromise events do not always mean that every attack is broad and indiscriminate. A smaller exposed group can still face concentrated attempts against email accounts, reused passwords, social media profiles, gaming accounts, or dating identities.
| Metric | Recent figure |
|---|---|
| Data compromises recorded in 2025 | 3,322 |
| Data compromises increase over five years | 79% |
| People affected in 2024 | 1.36 billion |
| People affected in 2025 | 278.8 million |
| Bogus or hijacked credit-card account complaints in 2025 | 597,770 |
| Password reuse among users exposed in multiple breaches | 60% |
| Password reuse among exposed .gov employees | 87% |
Credit-card abuse remains a major part of the reporting. FTC data summarized in Experian's FTC-based overview recorded 597,770 complaints in 2025 involving bogus or hijacked credit-card accounts. The same overview cites more than 3 million related fraud cases and over $15.8 billion in total losses in 2025.
Those figures describe more than stolen payments. Traditional identity fraud cost consumers $27.3 billion in 2025 and affected 18 million victims, according to a 2026 summary citing Javelin data. Account takeover victims reached 6 million, up 18% from 2024 (the cited Javelin summary).
The monitoring implication is specific: check both transactions and access. A bank alert may catch a fraudulent purchase, while an unusual login, password-reset message, changed profile detail, or new gaming or dating account can reveal misuse earlier. Attackers may need only one exposed credential and a few public clues to target a particular person rather than a large crowd.
What Happens When Your Identity Gets Used
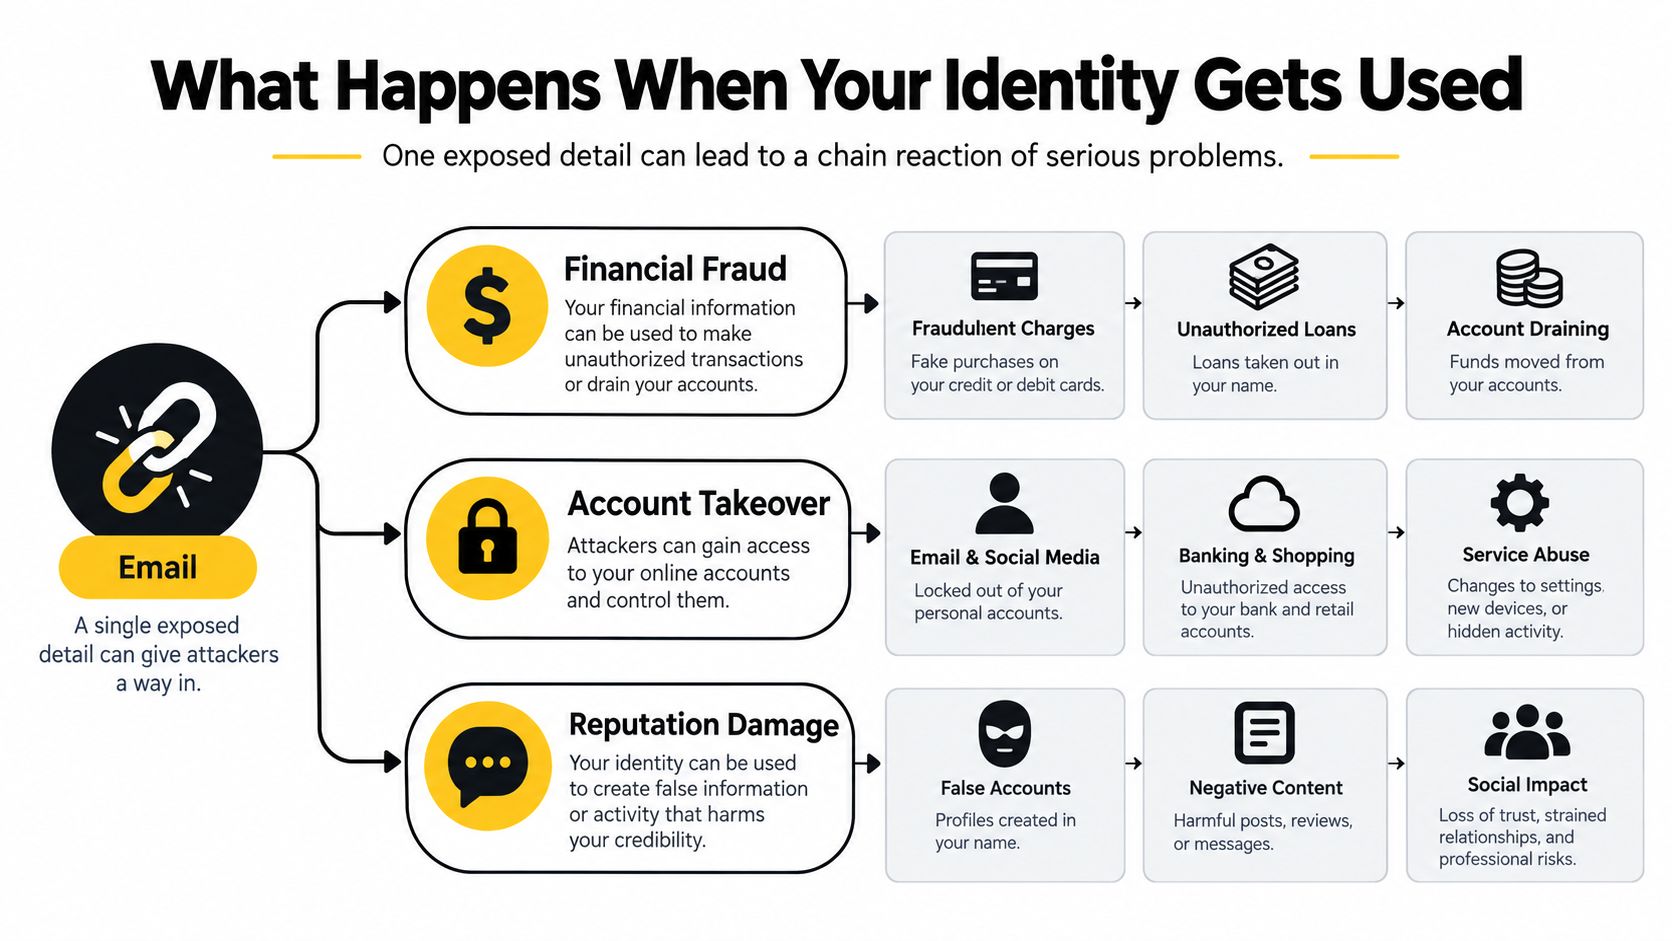
A single exposed detail can start a chain reaction. Consider a person whose old breach password remains active on an email account. An attacker tests it successfully, enters the inbox, and searches for password-reset links, bank notices, tax documents, workplace messages, and cloud-storage invitations.
The criminal doesn't need to understand the victim's whole life immediately. Email searches can reveal which services matter. From there, the attacker may reset a shopping account, change a social profile, contact friends, or send a convincing request to a colleague.
One compromise, several kinds of harm
Financial damage is the obvious pathway. The attacker may create an unauthorized account, make purchases, redirect payments, or use real information in a synthetic identity. Credit records, tax records, health information, and employment records can all become targets, but each creates a different recovery process.
Account takeover creates access damage. A stolen social profile can expose private conversations, change the visible name and photo, or send scam messages to friends. A hijacked gaming profile can threaten years of progress, purchased items, linked payment methods, and a reputation inside a gaming community.
Dating and social impersonation create a separate safety problem. A criminal may use someone's photos to build a convincing dating profile, collect personal details from matches, ask for money, or manipulate people under the victim's name. The Norton report on online dating scams states that 34% of current online daters said they'd been targeted by a scam, 64% of that group said they fell victim, and 36% reported pressure to send money to someone they met online.
Recovery becomes difficult because every consequence generates new evidence, notices, and disputes. The victim may need to secure accounts, contact financial institutions, challenge unfamiliar activity, preserve messages, and explain impersonation to friends, employers, platforms, or law enforcement.
The cascade isn't inevitable. It accelerates when one password or recovery method protects several accounts. MFA can sharply reduce compromise risk, but it isn't a complete answer. Microsoft's measurement study reported that MFA reduced compromise risk by 99.22% across users and 98.56% after a password had already leaked, while Proofpoint reported that 59% of accounts successfully taken over in 2025 still had MFA enabled (the MFA effectiveness analysis). Use phishing-resistant methods where possible and monitor sessions, devices, and recovery changes.
For a first-response checklist, use this guide to what to do after identity theft.
A Personal Risk Self-Assessment You Can Run Today
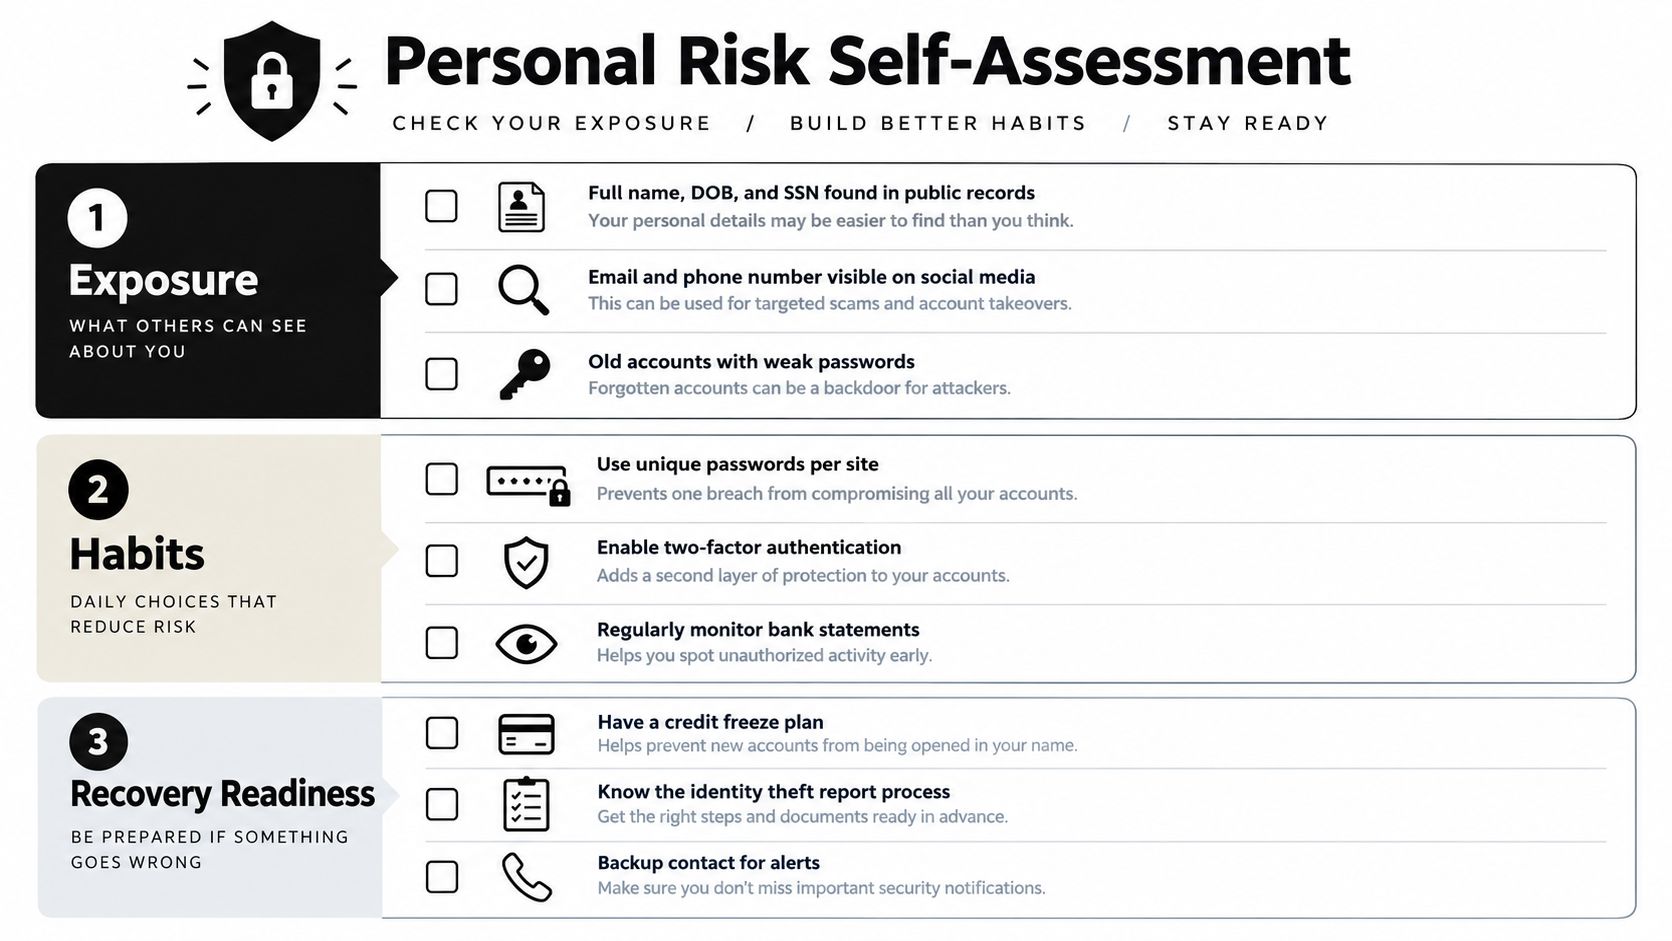
A useful self-assessment has three parts: exposure, habits, and recovery readiness. Treat it like checking which doors and windows are open before deciding where to add a lock. The result does not prove that identity theft occurred. It shows which uncertainty deserves attention first.
Start with exposure
Begin with your own public footprint. Search your full name, date of birth, home address, phone number, email address, employer, family names, and routine locations across public profiles, old forums, data-broker listings, and forgotten services. This OSINT-style review is the missing first step in many guides because identity misuse can reach social media, gaming profiles, and dating apps, not only bank accounts.
Ask yourself:
- Public details: Can a stranger connect your name to your address, relatives, workplace, or birth date?
- Old accounts: Do accounts from previous jobs, games, forums, or shopping services still exist?
- Breach exposure: Have you received notices about compromised credentials or personal information?
- Platform spread: Does the same username identify you across social, gaming, professional, and dating platforms?
A shared username can act like a signpost between services. An impersonator may use those connections to make a fake profile appear familiar to friends, teammates, customers, or dating matches.
Examine your habits
Password reuse needs a direct answer. If one password appears on several services, a breach at a low-value site can later threaten a high-value account. Check whether your primary email, password manager, banking, tax, health, workplace, cloud, gaming, and social accounts use unique credentials.
Review the controls that provide early warning:
- Authentication: Is MFA enabled, and can you use a passkey or security key?
- Alerts: Do banks and platforms notify you about logins, password resets, profile changes, and transactions?
- Recovery: Does your recovery phone or email remain current and protected?
Test recovery readiness
Confirm that you can still access your primary email and password manager. Keep account statements, identity documents, and incident records in a secure location, and know which institutions you would contact first.
A few exposed identifiers may indicate limited immediate exposure. Exposed details combined with reused credentials and missing alerts indicate greater concern. Neither result guarantees safety or proves theft. Use the findings to choose one action, such as changing a password, removing a public detail, securing a recovery channel, or beginning monitoring.
Use a personal digital footprint check to organize the review, then repeat it after a major account, phone number, or address change.
Your Defensive Playbook in the Right Order
Start with the accounts that control everything else. Your primary email and password manager often handle password resets, sign-in links, and recovery messages, so secure them before lower-risk services.
Use a password manager to generate unique, long passwords. Enable MFA on sensitive accounts, choosing passkeys or hardware security keys when available because they can resist common phishing techniques better than a password paired with a code. If you suspect a password has leaked, don't wait for suspicious activity. Replace it anywhere it was reused.
Work outward from the control center
After email and the password manager, secure banking, tax, health, workplace, cloud-storage, shopping, social, gaming, and dating accounts. Sign out unknown sessions, review recovery methods, remove unfamiliar devices, and confirm that profile details haven't changed.
Turn on login, transaction, password-reset, and new-account alerts. A credit freeze can restrict access to your credit file, but it won't stop a criminal from taking over an existing social account or impersonating you in a message.
Reduce the information strangers can assemble. Remove unnecessary birth-date details, home-location clues, family names, and routine posts from public profiles. Tighten privacy settings and submit removal requests to legitimate data-broker sites where appropriate.
Make deception harder to complete
Treat unexpected links, attachments, QR codes, and requests for verification codes as untrusted until independently confirmed. If a message claims to come from your bank, courier, employer, or a friend, contact that organization or person through a known channel. Don't use the phone number, link, or reply path supplied by the suspicious message.
Protect the devices that hold your identity. Install operating-system and application updates, use a strong screen lock, enable encryption where supported, back up important files, and avoid using administrator privileges for ordinary tasks. Review browser extensions and remove software you don't recognize.
Practical rule: An urgent request that asks for secrecy, a login, a code, money, or a gift card deserves verification outside the original conversation.
Prepare for response
Monitor credit reports, bank statements, account sessions, medical records, tax records, and search results associated with your name. Respond to unfamiliar accounts, charges, profile changes, and reset notices quickly. Save screenshots, emails, timestamps, and case numbers before deleting or blocking anything.
People managing staff, volunteers, or community access may also need a lawful, consent-based approach to identity verification. Verification should support safety and trust without encouraging unnecessary collection of personal data.
No single control removes the risk of identity theft. Layered defenses limit what each exposed detail can expose. For a broader checklist, review these personal cybersecurity best practices.
Monitoring Your Exposure with an OSINT Lens
OSINT means open-source intelligence, or gathering information from publicly accessible sources. Investigators use the approach to connect clues, and individuals can use a careful version of it to audit their own digital footprint.
Begin with identifiers you control. Search your email address in reputable breach-notification resources, check whether your phone number appears in exposed records, search usernames across platforms, and look for your name or address in data-broker listings. Review image results and old profiles too, because impersonators may reuse photographs or copy biographical details.
The point isn't to investigate strangers or collect private information about other people. A self-audit inventories what a criminal might discover about you.
Why inventory comes first
Many identity protection guides begin with passwords and monitoring. Those controls matter, but they're easier to prioritize after you know what is exposed. An old gaming username may reveal a linked social account. A public professional profile may identify your employer. A reused email can connect a dating profile, shopping account, and forgotten forum login.
A free OSINT checker can consolidate searches into one report rather than making you repeat the same lookup across many sites. Digital Footprint Check describes a scan covering 500+ platforms, including social networks, breach databases, gaming profiles, professional networks, and public records, so users can identify exposed information and hidden accounts. Treat any result as a lead to verify, not as proof that a listed record is accurate or current.
Financial concerns often overlap with privacy decisions, so readers comparing budgeting and protection tools may also want to compare financial wellness apps. Keep the categories distinct. A financial app can organize money habits, while an OSINT audit focuses on what information about you is publicly discoverable.
Run the free OSINT tools collection, review the findings, and assign each result a next step. Remove unnecessary public details, replace reused passwords, secure the associated account, and enable stronger authentication.
Living With the Risk and Common Questions
A reversed fraudulent charge doesn't necessarily end the risk of identity theft. The same email, phone number, username, image, or breached password may appear in a later scam, account-takeover attempt, or impersonation campaign.
The 2026 Trends in Identity Report summary reported that 25.6% of victims were dealing with two or more concurrent identity incidents, up from 23.5% the prior year. It also reported that unauthorized device access had overtaken scams as the primary threat for adults aged 35–64. That pattern supports a monitoring habit rather than a one-time cleanup project.
Does identity protection replace credit monitoring?
No. Credit monitoring can alert you to activity connected to credit files, but it doesn't cover every social, gaming, email, dating, device, medical, tax, or reputation problem. Use credit monitoring as one layer alongside account alerts, strong authentication, and an exposure audit.
How long does recovery take?
There isn't one dependable timeline. Recovery depends on the number of affected accounts, the type of misuse, the institutions involved, and whether the attacker still controls an email, phone number, or device. Document every contact, dispute, notice, and account change so you can show a clear sequence of events.
Is a credit freeze enough?
No. A freeze can help limit certain new-credit activity, but it won't protect an existing account from takeover or stop someone from impersonating you online. Secure email, devices, social profiles, gaming accounts, and recovery channels separately.
What should I do in the first 24 hours?
Secure your primary email and any compromised account, change reused passwords, contact the relevant financial institution, place a fraud alert with each bureau when appropriate, preserve evidence, and file a police report if the circumstances warrant one. Document everything, including dates, messages, account numbers, and case references.
For privacy-sensitive communication, review how a privacy-first alternative for privacy handles data before sharing sensitive details. Managing this risk is a habit, not a cure. Repeat an OSINT-driven self-check quarterly and whenever your key personal details change.
Digital Footprint Check helps you scan publicly accessible information across platforms, breach sources, data brokers, gaming profiles, and social networks so you can identify exposure before it becomes a larger problem. Run the free check at Digital Footprint Check, review the report, and use the findings to secure the accounts and personal details that matter most.