· Digital Footprint Check · Content Marketing · 15 min read
Open Source Intelligence Techniques Explained
Open source intelligence techniques for ethical footprint checks: search, metadata, usernames, records, verification, and legal limits.

OSINT can account for 80% to 90% of intelligence activities conducted by law-enforcement agencies and intelligence services in Western countries, according to estimates reported in a 2023 systematic review. That reframes public information: an ordinary photograph, forum post, or professional biography can become useful intelligence when someone connects it to a specific question.
For individuals, the same methods can uncover a gaming handle tied to a real name, an outdated professional profile, or photographs reused by a dating scammer. But finding a match isn't the same as proving identity. Responsible open source intelligence techniques combine discovery with verification, an audit trail, and a clear reason to stop.
Why Public Information Became Intelligence
Public information resembles breadcrumbs. A username is one crumb, a business filing another, a photograph a third. One crumb tells you almost nothing. A trail becomes meaningful only when someone collects the relevant pieces to answer a stated question.
Say you're applying for a job and want to know whether your public accounts expose information unrelated to your work. Searching your name produces scattered results. The analysis begins with three follow-ups: does each result belong to you, is it still current, and what could a recruiter reasonably conclude from it? Those same questions protect you in the other direction. A dating profile reusing your photos or a gaming handle matching your username should be treated as a lead rather than proof, because two strangers can share a name, a handle, or an old address.
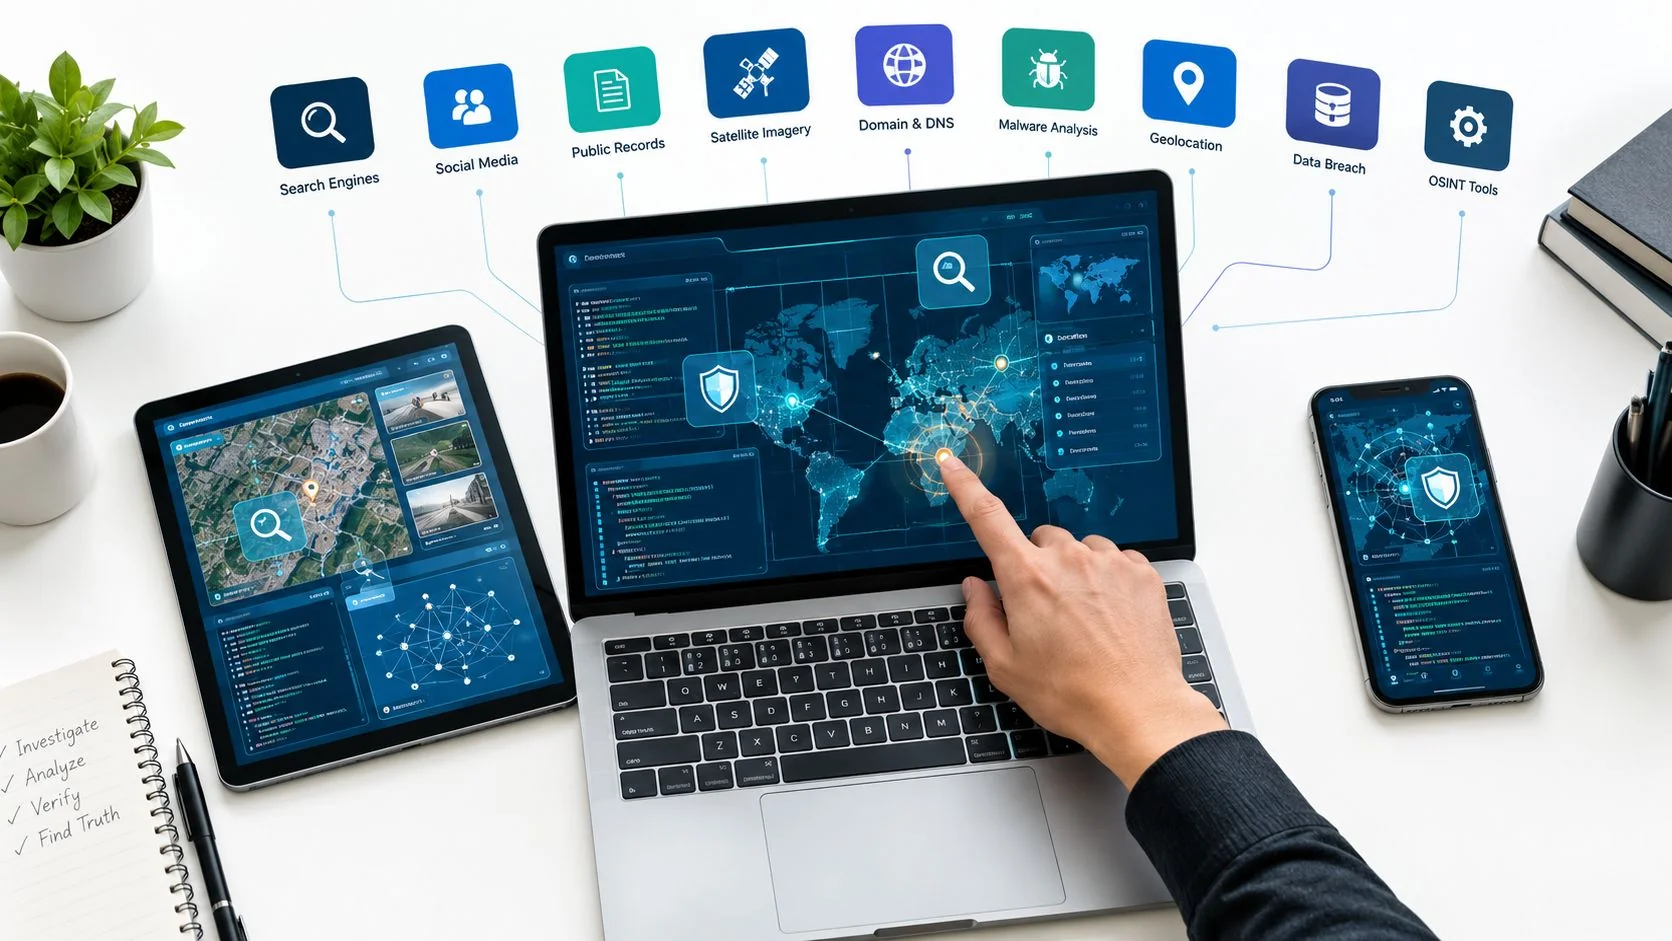
Intelligence work went through this same shift at scale. The share of material drawn from open sources varies by institution and by definition, but agencies now treat public material as a primary source rather than a supplement. Public-source work also draws on far more than social networks, as this overview illustrates.

A question turns information into intelligence
Open-source intelligence, or OSINT, means intelligence derived from publicly or commercially available information to address a specific requirement. The OSINT Foundation's account of official definitions explains that eligible information includes published media, websites, material available by request, subscription databases, casual public observations, and public meetings.
Paid access doesn't automatically place a source off-limits. The line sits between authorized access to available information and obtaining restricted information through deception, stolen credentials, or technical bypasses.
Your footprint also has two different origins:
- Active contributions include posts, comments, photographs, and information you deliberately submit.
- Passive or incidental traces include location information attached through settings and connections inferred from repeated identifiers. Choosing a handle is active; the cross-site association it enables may be unintended.
Practical rule: Define what you need to know before deciding what to collect.
Privacy concerns aren't unusual: a U.S. News & World Report survey reported by Biometric Update found that 91% of 2,000 U.S. adults surveyed in 2025 were concerned about information available about them online. A defined question and a clear reason to stop make that concern actionable without turning a self-audit into indiscriminate collection.
Six Techniques and Where Each Fails
Open source intelligence techniques at a glance
| Technique | What it can reveal | Typical public sources | Main failure |
|---|---|---|---|
| Search operators | Indexed pages, documents, and quoted-name mentions | Web indexes using site:, filetype:, and exact-phrase queries | Stale or duplicate copies treated as current |
| Metadata analysis | Capture time, device, orientation, and GPS if still present | Original photos and documents, not re-uploaded copies | Platforms strip or rewrite EXIF, so GPS can be missing or wrong |
| Social media reconnaissance | Public posts, bios, connections, and visible place clues | Profiles and posts that load without logging in | Private, deleted, or login-walled content is out of scope |
| Username and email correlation | Reused handles and public address appearances | Public profiles and already-public breach notices | The same string can belong to a different person |
| Public records | Filings, court indexes, and published addresses | Government and lawful commercial public databases | Name collisions, sealed files, and records outside the purpose |
| Image and geolocation checks | Whether a photo matches an earlier copy or a real place | Reverse-image search, maps, and visible landmarks | Reused, cropped, or synthetic images create false links |
Start with discovery methods
Search operators narrow the haystack. Put a name in quotation marks, use site: to focus on a particular website, or filetype:pdf to find documents. Open the underlying page before recording a conclusion, because a search snippet or cached copy may describe an older version.
Metadata analysis examines information embedded in files. ExifTool can display photographic fields such as capture time, camera model, orientation, and GPS coordinates. Preserve the original before inspecting it, and don't treat an empty location field as proof that a photograph was taken somewhere else.
Social media reconnaissance means reviewing visible posts, biographies, linked accounts, and contextual clues. A public connection isn't proof of friendship, employment, or agreement. For an ordinary privacy audit, stop when the next step requires a private group, login-walled content, or deleted material.
Treat connections as candidates
Username and email correlation finds repeated identifiers across public sources. An unusual handle is a useful search lead, but another person may have chosen it independently. Never test ownership by attempting password resets or entering exposed credentials.
Public-record searches can confirm that a filing or published address exists. They don't automatically establish that the person named is your subject. Check jurisdiction, dates, and relevant contextual details, while excluding sealed records and unrelated disputes.
Image and geolocation checks compare pictures with earlier copies and visible places. A reverse-image search for people can uncover photo reuse, but identifying the same photograph doesn't identify whoever controls an account. Cropping, reposting, and synthetic imagery all limit conclusions.
Choose one question, such as professional exposure or an inconsistent dating profile, and use only the methods that can answer it. You don't need every technique for every audit.
Run an Auditable OSINT Workflow and Verify Each Finding
Finding a match is the easy part. Establishing what that match means takes discipline. An auditable workflow works like a lab notebook: another person should be able to see the original question, repeat the lawful steps, inspect each capture, and understand why a finding was accepted, rejected, or left unresolved. A repeated handle, familiar photo, or matching email can support a lead; ownership still needs independent corroboration and a defined purpose.
An intelligence-methodology chapter from Springer divides the work into source evaluation, information credibility, collection, analysis, and reporting. Those stages keep a search result from being mistaken for an established fact.
Use this process chart as a collection-and-verification checklist.

Build the evidence trail
-
Write one intelligence requirement and its purpose limit. For example: can a public forum profile expose a workplace or residential area? Define the information needed to answer that question and exclude unrelated material, such as details about relatives. A clear purpose limit prevents incidental discoveries from becoming accusations.
-
Name allowed sources and stop lines. List public profiles, authorized databases, and relevant records before searching. Rule out private messages, restricted communities, deleted material, and access bypasses. A boundary written before the search is easier to honor when a tempting lead appears.
-
Preserve each observation. Record the URL, query terms, account context, UTC capture time, and visible metadata. Keep original files and, where lawful, create a cryptographic hash or read-only snapshot. A hash works like a tamper alarm because it can reveal later changes; proving that the captured content was authentic requires a separate assessment.
-
Normalize without erasing differences. Standardize date formats, document translations, and deduplicate records while retaining the originals. Spelling variations can otherwise split one person into several candidates, while duplicate pages can make weak support appear stronger.
-
Separate source reliability from information credibility. A reputable database can contain an outdated entry, and an unfamiliar account can publish an authentic primary file. Judge the source's track record separately from the evidence supporting the specific claim.
-
Corroborate identity attributes independently. Compare relevant details with professional profiles, official records, dated media, or legitimate breach notifications. Several websites copying the same biography still trace back to one claim and do not create independent confirmation.
-
Report observations, inferences, confidence, and unknowns. “The profile displays this handle” is an observation. “This person controls the profile” is an inference requiring additional support. Recording that distinction keeps a tentative connection from being treated as settled.
Test competing explanations
Once collection ends, argue against your own explanation. Ask what else could produce the same evidence. A shared name may identify several people, a copied image may connect pages without identifying their operators, and three reposts of one claim may provide less support than two sources with separate origins.
For this workflow, require two unrelated sources and a matching timeline before considering a high-confidence identity link. Treat this as a conservative reporting rule because conflicting evidence can still require a lower rating.
Reverse-image hits may reveal earlier copies while leaving the original unknown. Edited or deleted posts may be impossible to reproduce. Repeated claims may be an echo rather than corroboration.
Treat EXIF data as changeable evidence. For location claims, compare visible signs, roads, landmarks, and shadow direction with maps and plausible capture conditions; leave the location unresolved when those details conflict.
Authenticity deserves its own check. NIST's January 2025 evaluation of analytic systems against AI-generated deepfakes addresses this forensic problem. A convincing face or plausible voice still needs provenance and corroboration.
Auditable OSINT turns open data into evidence another person can inspect.
The standard matters most when the result could affect hiring, dating, safety, or reputation decisions. A due diligence investigation with inspectable reasoning should show the evidence, alternatives considered, confidence level, and remaining limits before anyone acts on it.
Use the video as a visual walkthrough, comparing each step with your written checklist and pausing whenever a lead lacks capture details or independent support.
Walk One Pivot From Gamer Tag to Verified Lead
Say you use the fictional handle CedarQuestPilot and want to know whether strangers can connect it to your real name. The requirement is narrow: identify public links between that handle and your name, not discover everything about everyone you've played with.
Private friend lists and login-walled chats are out of scope. A cross-platform username search is a starting point, not an identity verdict.
Follow the visible connection
Search the exact handle in quotation marks and inspect public profile pages. Save each relevant URL and UTC capture time. A forum profile displaying the handle is an observed occurrence, even if you don't yet know who controls it.
Run a reverse-image search on its avatar. Suppose the picture also appears on a photography page under a real name. Record the reused image, but don't assume the named photographer owns the gaming account.
Compare the gaming biography, linked social account, and screenshot details with the handle's visible history. If the biography links directly to a public social profile, preserve that link rather than relying on a matching display name.
Your working notes might distinguish:
- Observed: The gaming profile displays the handle and links to a named public account.
- Candidate: A photograph also appears on a page bearing that name.
- Unresolved: The player, photographer, and named account owner may not be the same person.
Stop before certainty outruns evidence
Search the candidate in an independent professional profile or dated local news item. Relevant agreement can justify an inferred connection, but it may still fail to establish control of the gaming account.
Write the report with low confidence if the chain rests on a handle match and reused photograph. The verified lead is that a public association exists, not that identity has been proved.
For your own account, remove unnecessary location clues and separate the gamer tag from your real name. If someone has copied your identity, report impersonation through the platform rather than publicly accusing the candidate account owner.
What These Checks Change in Real Life
Jobs and dating
A job applicant discovers an old portfolio that lists a different job title from their résumé. A recruiter can encounter that public page without knowing its history. The mismatch may be innocent, but it creates a question the applicant can resolve by updating the page or adding accurate dates.
Keep the audit focused on professional presentation, not unrelated personal characteristics. Action: reconcile public work information with the résumé you're submitting.
A dating-app user receives affectionate messages followed by an urgent request for cryptocurrency. A Justice Department warning citing FBI data reported approximately 59,000 romance-related scam victims in 2024, with reported losses exceeding $672 million. The financial stakes justify caution without assuming every inconsistent profile is fraudulent.
Compare the person's photograph, username, employment claim, and stated location. A rapid move off-platform, avoidance of reliable verification or a safe public meeting, an emergency story, and requests for money should prompt caution. Preserve messages and transaction records, stop sending money, and report the account without attempting to access it.
Gaming and identity theft
A multiplayer gamer uploads a victory screenshot containing a recognizable location clue. In the Anti-Defamation League's 2021 survey, 83% of adults aged 18–45 who played online multiplayer games reported harassment during the previous six months; 22% reported being doxed and 20% reported being swatted. Doxing exposes identifying information, while swatting uses a false emergency report to trigger a law-enforcement response.
These are self-reported survey experiences, not predictions for every player. They nevertheless make gaming-profile privacy a personal-safety concern. Action: remove identifying details from profiles and screenshots, including unnecessary links to real-name accounts.
An account holder finds their email in a legitimate breach notification. That indicates possible exposure associated with the address, not proof that every matching public account belongs to them. Secure the affected account through its official website.
NIST's guidance for individuals recommends enabling multi-factor authentication wherever available. MFA combines different factor types, such as a password and a security key, rather than merely adding another password. Action: replace the exposed password and enable MFA.
A successful login proves something about access, not everything about identity.
That distinction applies across these situations. NIST's digital-identity framework treats authentication and identity proofing as separate parts of an identity system. A badge, phone check, or selfie shouldn't settle unrelated claims about someone's work, location, or intentions.
Ethical and Legal Lines for Ordinary People
Public doesn't mean unrestricted permission. Being able to view a record doesn't settle whether you may collect it at scale, retain it, republish it, or use it to make an employment decision.
In February 2025, the European Ombudsman opened an inquiry concerning access restrictions on documents about social-media and OSINT monitoring conducted by Europol with Frontex. The inquiry illustrates contested transparency around monitoring; it isn't a blanket ruling that all OSINT is unlawful.
Keep these boundaries visible while collecting information.

Collect for a purpose, not a dossier
Stop when another record won't answer your written question. Exclude health, religion, political activity, and information about children or relatives unless that information is the lawful subject of the work and strictly necessary.
Document the applicable lawful basis, obtain consent where appropriate, and establish a retention limit. Laws vary by jurisdiction and purpose, so a self-audit and an employer's screening process don't have identical obligations.
Platform rules matter too. HarvestMyData's explanation of when website terms restrict scraping provides context for reviewing collection methods before automating them. Terms, privacy duties, and access restrictions need separate attention.
More data can make a decision worse when irrelevant associations look like evidence.
A practical understanding of whether OSINT is legal starts with the proposed action, not merely the source's visibility.
Build a correction path
Before sharing a report, specify how someone can challenge an incorrect link and how you'll correct or delete it. Limit access to people who need the findings, and require human review before consequential action.
Use these stop conditions:
- Purpose missing: Don't collect until the question and boundaries are written.
- Sensitive fields unnecessary: Exclude them instead of retaining them just in case.
- Independent support missing: Don't present an identity link as confirmed when the corroboration rule hasn't been met.
- Appropriate notice absent: Pause consequential use until notification and challenge arrangements are addressed.
- Restricted access required: Stop before passwords, private accounts, or technical bypasses become necessary.
Check Your Own Footprint Before Someone Else Does
A self-audit gives you room to correct exposure before another person misinterprets it. Keep the task small enough that you can verify findings and complete the cleanup.
Run a focused self-audit
-
Choose your question and identifier. Search your own username or email to assess one concern, such as professional visibility, dating-profile reuse, or a gaming identity connected to your name.
-
Review potential matches. Label each finding observed, inferred, or uncertain. Don't merge accounts merely because their names resemble yours; retain only evidence relevant to the question.
-
Act on confirmed exposure. Update an inaccurate professional profile, remove location clues, report an impersonating account, or replace an exposed password through the legitimate service.
For social-account cleanup, account privacy advice from Unfollowers Track offers a practical guide to making Instagram private. Review existing followers and visible profile details too, rather than assuming a setting resolves every exposure.
Our guide to checking your digital footprint can help you organize follow-up work.
Use discovery without outsourcing judgment
Digital Footprint Check starts with a username or email, presents potential matches, and provides step-by-step actions. Our reports can reveal social profiles, gaming accounts, forum activity, breach exposures, public records, email appearances, dark web mentions, and more across 500+ data sources.
The free Profile Checker, Username Search, Data Breach Checker, and Reverse Email Search are available through the free-checker tools. The free preview has limited features; paid plans provide fuller phone, social, gaming, and web reporting.
Results depend on what you enter and which sources are available. No search guarantees a complete picture. Audit yourself first, keep only what serves your purpose, and correct false matches before they affect a job, relationship, or your safety.
Digital Footprint Check helps you discover potential public matches and turn findings into practical privacy actions. Start with your own username or email, verify the connections that matter, and address confirmed exposure rather than treating every result as proof.